#111 · Customizable Security Test Settings Now Available for API and Frontend DAST
Different organizations have different risk tolerances and prioritization needs. To support this, Escape now lets you configure which security tests are enabled—and how they're prioritized by severity—across your entire organization.
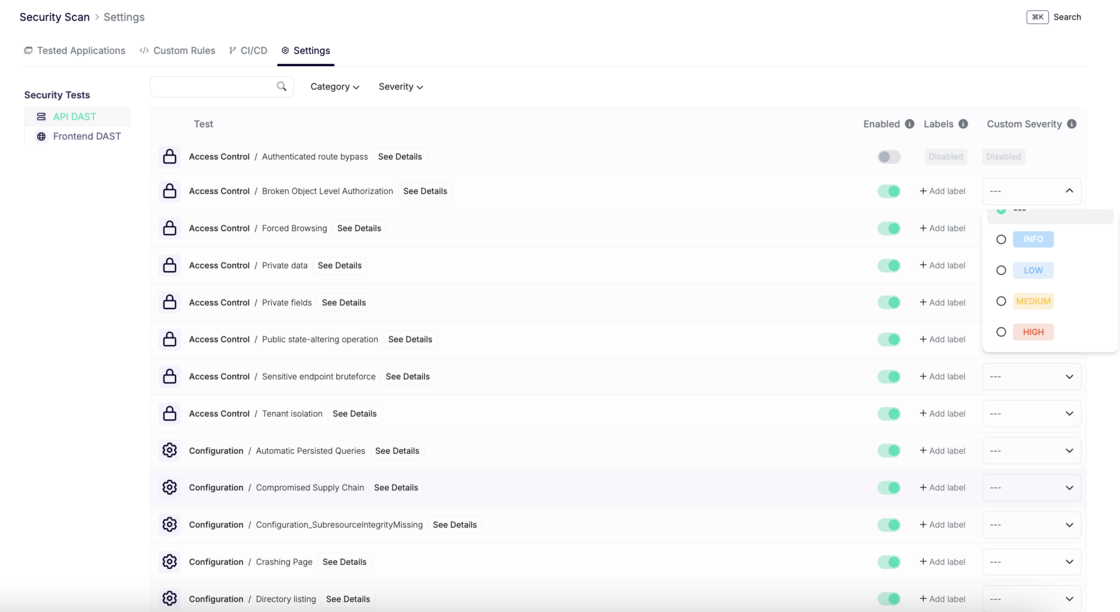
What’s new:
- A new Test Configuration page is now available for both API DAST and Frontend DAST.
- It provides a full list of security tests, where you can:
- Enable or disable each test.
- Assign a custom severity level: Info, Low, Medium, or High.
How it works:
- Custom severities override Escape’s default severity scoring, which is based on exploitability, CVSS score, vulnerability type, and other risk factors.
- These settings apply at the organization level, ensuring consistency across all scans.
What you’ll gain
- Tailor testing to your specific compliance and internal needs.
- Reduce noise by disabling less relevant tests or deprioritizing less critical findings
- Establish consistent prioritization logic across teams and applications