Skip to content

2023

#34 · Enhanced Scanning Capabilities through Insomnia Collections & WP-JSON Schema support 🌐

We're excited to share a significant expansion in our Dynamic Application Security Testing (DAST) capabilities. Escape now supports a broader range of input formats, catering to diverse API testing needs and environments. πŸ› οΈ

Expanded Input Support πŸ”

  • Insomnia Collections: Extend your DAST capabilities to include Insomnia Collections, enabling seamless security testing for those utilizing this popular API tool.
  • WP-JSON Schema: Specifically for WordPress users, we now support WP-JSON Schema, enhancing security testing for WordPress-based APIs.
  • Continued Support for Existing Formats: Our DAST feature maintains its robust support for:
    • Swagger v2
    • OpenAPI v3
    • Postman Collection
    • GraphQL Introspection
    • GraphQL Schema

Why This Matters? 🌟

  • Broader Testing Reach: Cover a wider range of API formats, ensuring comprehensive security coverage across different platforms and tools.
  • Versatility in Security Testing: Adapt to various API design and documentation practices, offering flexibility and precision in security testing.
  • Ease of Integration: Smoothly incorporate these new formats into your existing security workflows, enhancing efficiency without compromising on thoroughness.

πŸ” Your Security, Our Commitment We continue to evolve our DAST capabilities to keep pace with the dynamic world of API security. Stay tuned for more updates as we constantly strive to provide top-tier security solutions.

Stay Proactive, Stay Secure!
#33 · New AI-Powered Business Logic Security Tests for Enhanced Access Control 🧠

We're proud to introduce a suite of advanced AI-powered security tests at Escape Tech, specifically designed to fortify access control in your applications. Leveraging state-of-the-art artificial intelligence, these tests are engineered to uncover complex business logic vulnerabilities and attack chains with unprecedented precision. πŸ€–

Cutting-Edge Security Checks πŸš€

  • Automated Tenant Isolation Control: When two users are configured, this test ensures strict tenant isolation, preventing unauthorized cross-tenant access.
  • Sensitive Endpoint Brute Force: Targets critical endpoints like login and reset-password, safeguarding against brute force attacks.
  • Broken Object Level Authorization (IDOR) Checks: Identifies vulnerabilities in object-level authorizations, an essential aspect of access control.
  • Enhanced Access Control Checks: Overall improvements in access control validations, providing a more robust security posture.
  • Public State Altering Operation Identification: Ensures that operations altering application data (like REST READ, UPDATE, DELETE requests, and GraphQL mutations) are adequately protected by authentication middleware.

The AI Edge 🌐

These tests utilize advanced AI algorithms to generate complex sequences of requests, meticulously uncovering and exploiting business logic flaws and potential attack vectors. This approach allows for the detection of intricate vulnerabilities and attack chains that conventional methods might miss.

Compatibility and Documentation πŸ”—

  • REST & GraphQL Compatibility: Our security tests are compatible with both REST and GraphQL APIs, ensuring comprehensive coverage across different API architectures.
  • Detailed Documentation: Dive into our comprehensive guide to understand how these AI-powered tests can be integrated into your security strategy.

Elevating Security Intelligence 🌟

By harnessing AI in security testing, we're pushing the boundaries of traditional cybersecurity measures. These enhancements reflect our commitment to providing cutting-edge, intelligent solutions in the ever-evolving landscape of cyber threats.

Stay Ahead of Threats with AI-Driven Security!

Escape Team

#32 Β· Create New Applications in DAST Automatically via API! πŸ”₯

Exciting news from Escape Tech! You can now create new Applications in our Dynamic Application Security Testing (DAST) service directly through the API. This update is all about enhancing your workflow efficiency and simplifying your security testing process. πŸ› οΈ

Key Features of the API Route πŸ—οΈ

  • Flexible Application Settings: Define your application's specifics, like name, type (GraphQL or REST), and server URL.
  • Schema Customization: Provide your application's schema as a string or through a public schema URL.
  • Adaptable Scan Settings: Fine-tune your scans with settings like read/write access, customizable for safe production scans.
  • Authentication Support: Add authentication details for scanning, with options for different user names and authorization headers, or opt for no authentication.
  • Optional Repeater Use: Integrate a repeater if needed for your scanning requirements.

Advantages for You 🌟

  • Streamlined Integration: Add new applications to DAST quickly and efficiently via API.
  • Diverse API Support: Compatibility with both GraphQL and REST applications.
  • Tailored Scanning Options: Customize scans for precision and safety.
  • Simplified Authentication Setup: Easy setup for various authentication scenarios.

πŸ”— Check out the full API documentation here for detailed instructions and more info.

πŸ” Elevating Your Security, Simplified Our commitment to enhancing your security processes continues. This new feature demonstrates our dedication to providing flexible and comprehensive security solutions.

Happy Secure Coding!

#31 Β· API Inventory under steroids πŸ’«

Hello, API Security Mavericks! πŸ› οΈ

After the successful launch of our API Inventory, we're excited to unveil its latest evolution with enhanced capabilities and integrations. Our commitment to providing comprehensive API security has led to significant additions to our Inventory feature. 🌐

What's New? πŸ”Ž

  • Postman Integration: Seamlessly integrate with Postman to find and manage Postman Collections directly within Escape.
  • GitHub Integration: Automatically discover OpenAPI schemas in your GitHub repositories, enhancing your security oversight in code repositories.
  • Enhanced Schema Detection: Advanced automation now identifies exposed schemas on the internet, bolstering your external security posture.
  • API Framework Discovery: Identify the frameworks behind your REST and GraphQL APIs, adding another layer to your security insights.
  • Cloud Provider Identification: Determine which Cloud Provider (AWS, GCP, and more) is hosting your APIs, supporting a broad range of providers.
  • Environment Tagging: Easily distinguish between production and staging endpoints, ensuring appropriate security measures are applied.

Extended Benefits 🌟

  • Comprehensive API Coverage: With these new integrations and capabilities, gain a more holistic view of your API landscape.
  • Automated Insights: Reduce manual workload with automated discovery and categorization of APIs, improving efficiency and accuracy.
  • Strategic Security Posture: Tailor your security strategy with detailed information on API frameworks, cloud providers, and environment types.

πŸ“£ Stay Tuned for More! We're constantly enhancing our platform to ensure you stay ahead in the cybersecurity race. Keep an eye out for future updates and features!

Stay Secure and Informed! πŸ”’

#30 Β· [Enterprise] Fine-Grained Role-Based Access Control (RBAC) πŸ›‘οΈ

We're thrilled to announce a major update that's set to enhance your experience and security management capabilities with Escape: the transition from Policy-Based Access Control (PBAC) to a more sophisticated and flexible Permission-Based Access Control (RBAC) system. πŸ”„

What's New? πŸ”

  • Fine-Grained Control: Assign specific permissions to roles and directly associate these roles with users. This granular approach ensures tighter security and tailored access rights.
  • Enhanced Feature Access: Gain more control over various Escape features, including:
    • Organization Management: Administer your organization's settings with precision. πŸ”§
    • Inventory Oversight: Keep a meticulous track of your inventory with enhanced access control. πŸ“Š
    • Application Access: Manage access to all scanned applications with ease. πŸ“±
    • Reporting Capabilities: Generate and access reports with adjustable read and write permissions. πŸ“ˆ
    • Integrations Flexibility: Seamlessly integrate and manage external tools and services. πŸ”—

Built for Enterprise: This update is especially tailored for our enterprise customers, enhancing your team's collaboration and security governance.

SSO Integration: The new RBAC system works hand-in-hand with Single Sign-On (SSO), providing a streamlined and secure user experience. 🀝

As always, we're committed to providing you with the best tools to secure your digital landscape. This update reflects our dedication to offering customizable, robust security solutions.

Stay Safe, Stay Secure! πŸ”

#29 Β· Enhanced Application Management with Search, Filtering, and Tagging!

As we continue to grow and serve larger organizations, we've recognized the need for more advanced application management features. With a vast number of apps, sifting through to find what you're looking for can be cumbersome. Enter our new suite of tools designed to simplify and enhance your application management experience!

🌟 Key Highlights:

  1. Powerful Search Capabilities: Quickly find the application you're looking for with our optimized search function. Never lose sight of any app again!

  2. Dynamic Filtering:

    • By Technology: Easily categorize and view applications based on their technology stack.
    • By Risk: Prioritize and manage apps based on their risk levels to ensure you're focusing on what matters most.
  3. Custom Tagging: Beyond the default filters, tag your applications with custom labels that matter to your organization. It provides advanced filtering options tailored just for you!

πŸš€ Why It Matters:

With an increasing number of applications, ensuring that you can easily access, manage, and categorize them is essential. These new features not only help declutter and organize your apps but also streamline workflows and improve overall productivity.

πŸ“š Dive Deeper:

Dive into the specifics of these new features and learn how to leverage them to their full potential by checking out our comprehensive guide (link to be added).

πŸ“’ We're Listening:

Your input is invaluable. Let us know how these new application management tools are enhancing your experience, and share any additional features or tweaks you'd like to see in future updates!

#28 Β· πŸ“„ Export Compliance Reports as PDF

Taking another leap forward, we're thrilled to present the PDF Compliance Report feature in Escape. The capability to seamlessly export and manage compliance reports is an essential tool for organizations, and we've made it even more streamlined and efficient!

🌟 Key Highlights:

  1. Individual Export: Navigate to the Compliance Tab and instantly export individual compliance reports as PDFs. Quick, efficient, and hassle-free!
  2. Bulk Download: Time is valuable! Directly download all the reports in one go under the Pentesting Report. No more waiting or multiple clicks!
  3. Compliance Coverage: We're rolling out with support for prominent compliances including OWASP TOP 10, CWE, PCI-DSS, and WASC. This ensures you're aligned with industry benchmarks and best practices.
  4. Stay Tuned: Our commitment to enhancing the user experience is unwavering. Expect more compliance reports to be added in the near future!

πŸš€ Why It Matters:

Compliance isn't just about checking boxes; it's about ensuring the security and trustworthiness of your systems. With the PDF Compliance Report feature, not only can you efficiently track and manage your compliance status, but also easily share and communicate these reports within your organization or with external stakeholders such as auditors or customers.

πŸ“š Dive Deeper:

To explore further and understand the intricacies and benefits of the PDF Compliance Report feature, head to our detailed documentation (link to be added).

πŸ“’ We're Listening:

Your insights and feedback have always been the cornerstone of our continuous evolution. Share your thoughts on the PDF Compliance Report feature, and together, let's make the digital landscape more secure and compliant!

#27 Β· [Enterprise] Scan Internal APIs with Elevated Ease Using Escape's Repeater Agent

Dive into an advanced layer of internal API scanning with the introduction of Escape’s Repeater Agent. While the proxy method for scanning internal APIs has been steadfast, our advancement to enhance your experience, especially for our Enterprise customers, has brought forth the Agent.

🏹 Repeater Agent: Your Gateway to Robust Internal API Scanning

The Repeater Agent serves as a powerful facilitator to scan Internal Apps, securely situated behind your organization’s firewall or VPN, by forming a private tunnel between Escape and one of your servers. This means all the requests from Escape are strategically channelled through your server, offering you a seamless, secure, and highly efficient internal API scanning mechanism.

🌐 Workflow Insight:

  1. Repeater Client Connection: Your locally deployed repeater client connects to the repeater manager.
  2. Scan Initiation: When a scan kicks off on Escape, requests are sent to the repeater manager, instead of directly to your server.
  3. Request Transfer: Your client receives and forwards them to your server.
  4. Result Transmission: Scan results are transmitted back to Escape, ensuring you have a clear view and control of your scans’ outcomes.

πŸ› οΈ Setup and Utilization:

  • Efficient Setup: Craft a new repeater through the Escape interface and retrieve its repeater ID for setup.
  • Repeater Client Configuration: Employ the repeater client on your server, following the guidelines provided in the readme of the repeater client.
  • Application Configuration: Adapt your applications with a simple configuration snippet, utilizing the repeater ID.

πŸ“˜ Dive into the Documentation:

Navigate through a detailed guide on leveraging the Escape Repeater Agent for meticulous internal API scanning by visiting our documentation. Your path to understanding and implementing this feature adeptly begins here!

πŸš€ Propel Forward:

With the Repeater Agent, drive your security scanning into a domain of enhanced control, efficiency, and security. Your journey towards fortified application security is robustly supported with features that prioritize your organizational needs and challenges.

Your feedback fuels our innovations. Share your experiences and journey with the Repeater Agent, and let’s continue advancing towards a secure digital horizon together!

#26 · 🎯 Elevate Your Security Focus with Risk Contextualisation and Prioritization

Introducing a pivotal feature in Escape that transforms your security management strategy: Risk Contextualization and Prioritization. Merging the power of Escape’s distinctive Inventory and DAST features, we’re enabling AppSec Engineers to pinpoint and prioritize what genuinely requires immediate attention.

πŸ™‰ The Objective:

Ensure that your focus and remediation efforts are efficiently targeted. An SQL Injection on a route manipulating sensitive data, especially when exposed to the internet, demands priority – and we ensure you recognize such issues upfront.

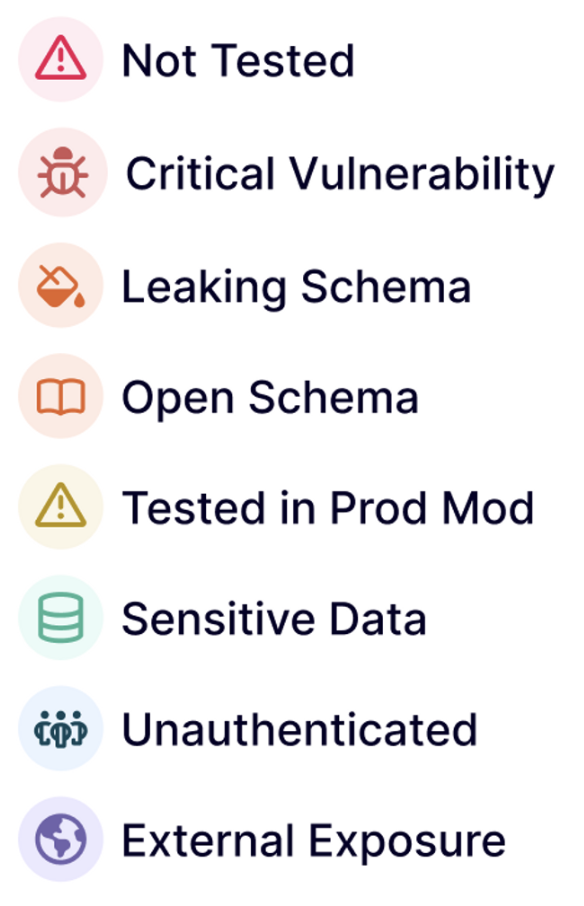
🚨 Risk Categories:

Navigating through risk becomes seamless with categorization that empowers you to identify and tackle vulnerabilities adeptly.

CleanShot 2023-10-03 at 11.57.25@2x.png

πŸ”Ž See it in Action:

Direct your attention and resources where it truly counts by honing in on critical, sensitive, and potentially exposed endpoints that could pose significant risks.

Let’s Continue Together:

Your security journey is our priority. With features designed to streamline your risk management, we're committed to offering a platform where your security endeavors are intuitive, strategic, and impactful. Share your experiences and let’s bolster our path towards sophisticated and accessible application security!

#25 Β· Escape for REST APIs in General Availability

πŸš€ REST API Scanning Now Available in Escape

We're thrilled to announce that Escape now supports GenAI-powered DAST Scanning in CI/CD, extending our capabilities to REST APIs alongside our existing GraphQL API offerings. Implementing security practices into your CI/CD pipeline has never been so straightforward!

βš™οΈ What's New:

  • 1. Extended API Support: Your REST APIs are now in safe hands with our advanced DAST scanning, which is now compatible with both REST and GraphQL APIs.
  • 2. Diverse Input Options: Catering to a variety of workflows, Escape accepts input from OpenAPI, Swagger, or Postman, with more options en route.
  • 3. Business Logic Testing: We're not just scanning - we're ensuring that your API's business logic and complex attack scenarios are thoroughly vetted.
  • 4. Comprehensive Security Tests: With more than 50+ security tests now supported, we're ensuring your APIs are fortified against vulnerabilities.

For a comprehensive view of our available security tests, check out our documentation.

πŸš— Taking it for a Spin:

Dive right into your API scanning and start fortifying your REST APIs alongside your GraphQL APIs. Ensuring comprehensive API security has never been this accessible or thorough.

In Closing:

As we pave the path toward robust API security, your inputs are invaluable. We're here to support your API – REST or GraphQL, and provide a secure, resilient environment for your applications. Share your feedback and let's continue this journey toward impregnable API security together!