#68 · Escape + Wiz: Unified Security for Modern, Cloud-Native Applications
We’re excited to announce our new integration with Wiz, bringing together Escape’s deep application-layer insights with Wiz’s unparalleled cloud security capabilities. This partnership empowers security teams with:
- Practical Code-to-Cloud Security: Large organizations often struggle to bridge application-level exposures with cloud infrastructure insights. Now, they can see both in one place, track them back to the same responsible teams, and reduce friction between dev, ops, and security.
- Immediate Assignment: The moment Escape flags a security issue, you know exactly which team needs to address it. No more guesswork, no more rummaging through outdated confluence pages or domain registries.
- Acceleration of Remediation: When ownership data is at your fingertips, the gap between detection and remediation shrinks from weeks or months to days or even hours. It’s not just about finding vulnerabilities; it’s about fixing them fast. This empowers you to integrate security into applications early in the development lifecycle confidently.
- Reduced Operational Overhead: Security Engineers spend less time “hunting” for who owns what. Instead, they can devote their energy to actually securing the organization. That leads to more strategic work, less administrative burden, and a meaningful drop in burnout.
How it works:
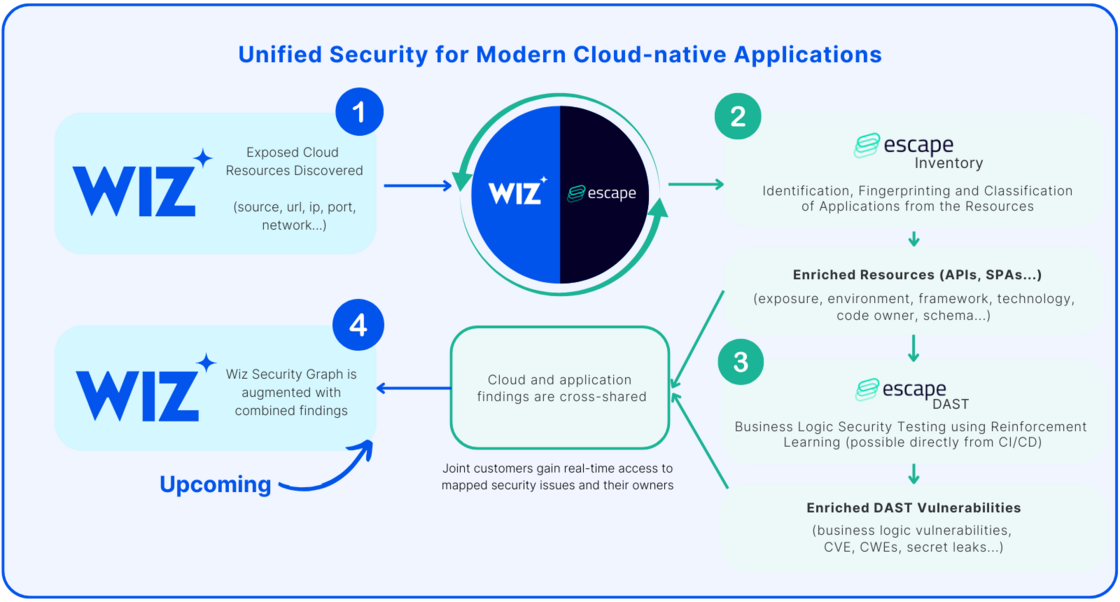
- Wiz External Attack Surface Management finds exposed cloud resources and hands them over to Escape.
- Escape Inventory then identifies, fingerprints, and classifies these resources as specific application assets—such as APIs, Single-Page Applications (SPAs), and more.
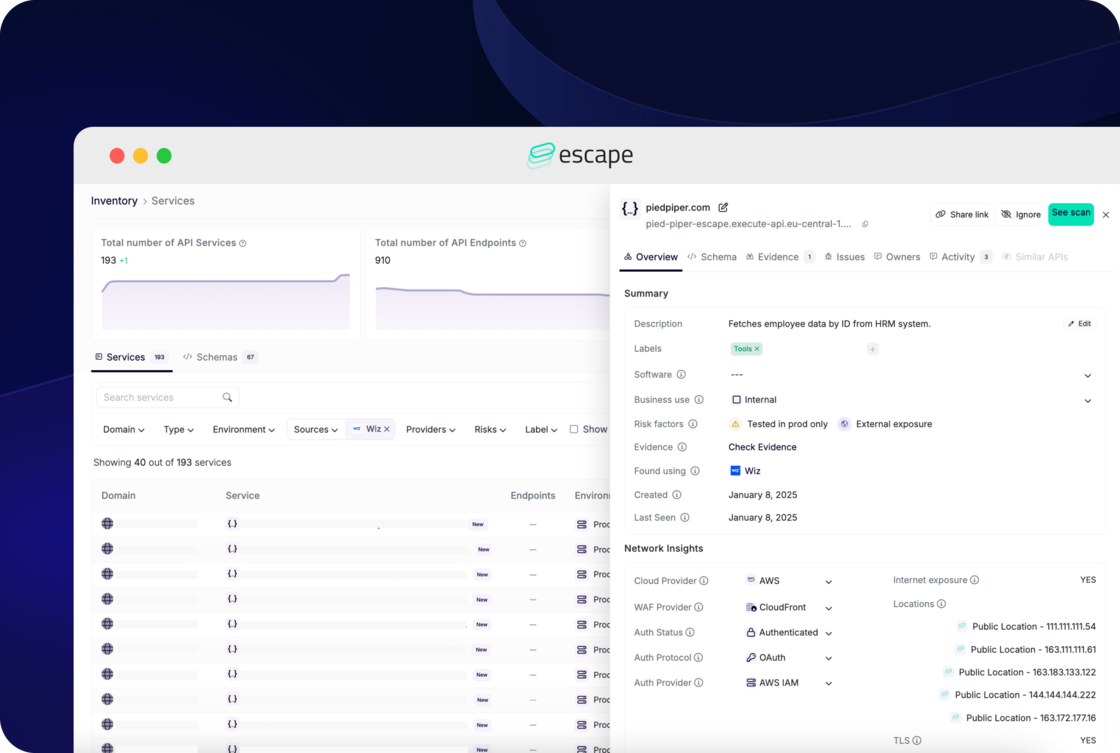
- With this enriched information, Escape DAST runs at scale on the identified applications, including APIs, without needing any network interception or agent installation.
💡 If you're a joint Wiz and Escape customer, you can find step-by-step instructions on how to set up Wiz integration in the Escape's official documentation. Feel free to set it up now 😉