#85 · Bi-directional Integration with Wiz
Our bi-directional integration with Wiz is now live!
Using previously ingested and enriched Wiz resources, Escape DAST identifies business logic vulnerabilities, API misconfigurations, and sensitive data leaks, then feeds these findings—including CWE classifications and remediations—directly into Wiz.
This integration enriches security teams with valuable context and ownership data, enabling them to prioritize and remediate vulnerabilities more effectively. With this unified solution, organizations can detect risks quickly, gain clear ownership insights, and confidently embed security early in the development lifecycle.
Here's how it works:
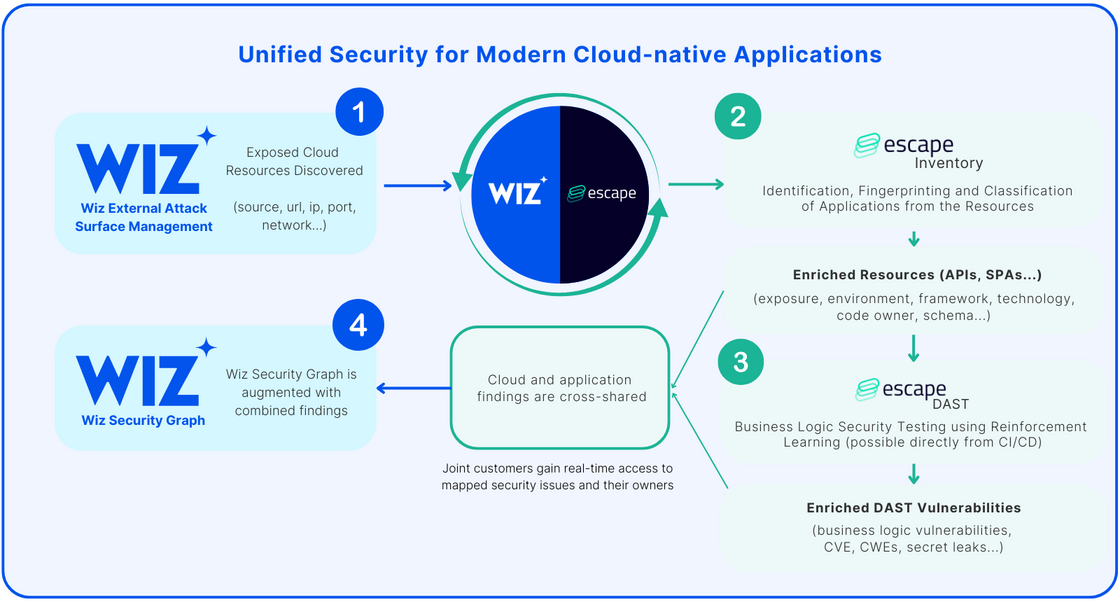
- Wiz's Dynamic Scanner finds exposed cloud resources and hands them over to Escape.
- Escape Inventory then identifies, fingerprints, and classifies these resources as specific application assets—such as APIs, Single-Page Applications (SPAs), and more.
- With this enriched information, Escape DAST runs at scale on the identified applications, including APIs, without needing any network interception or agent installation. If you're a joint Wiz and Escape customer, you can find step-by-step instructions on how to set up Wiz integration in Escape's official documentation
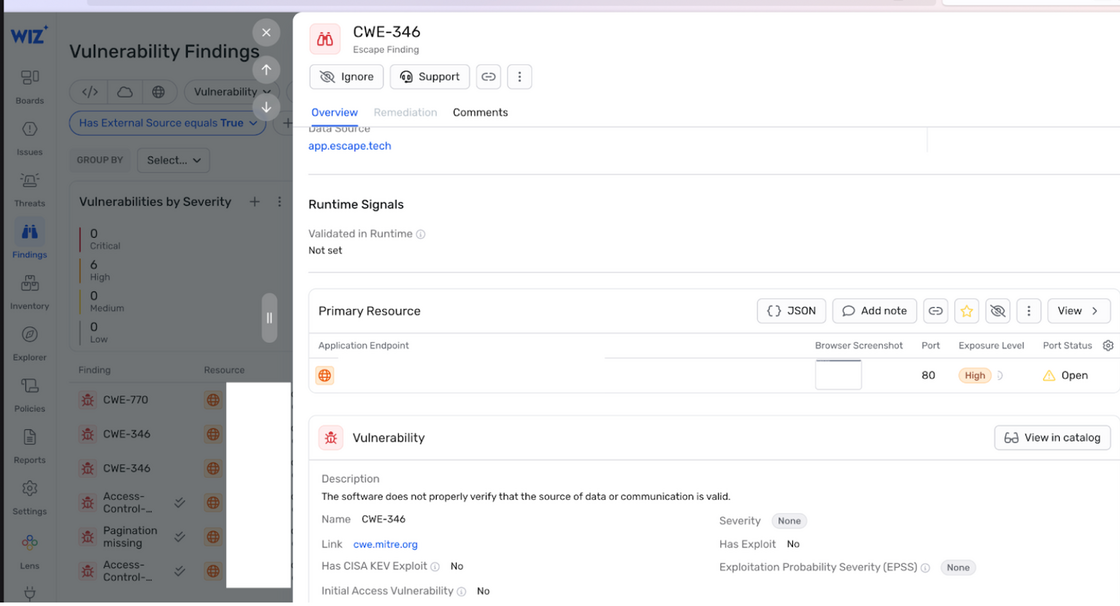
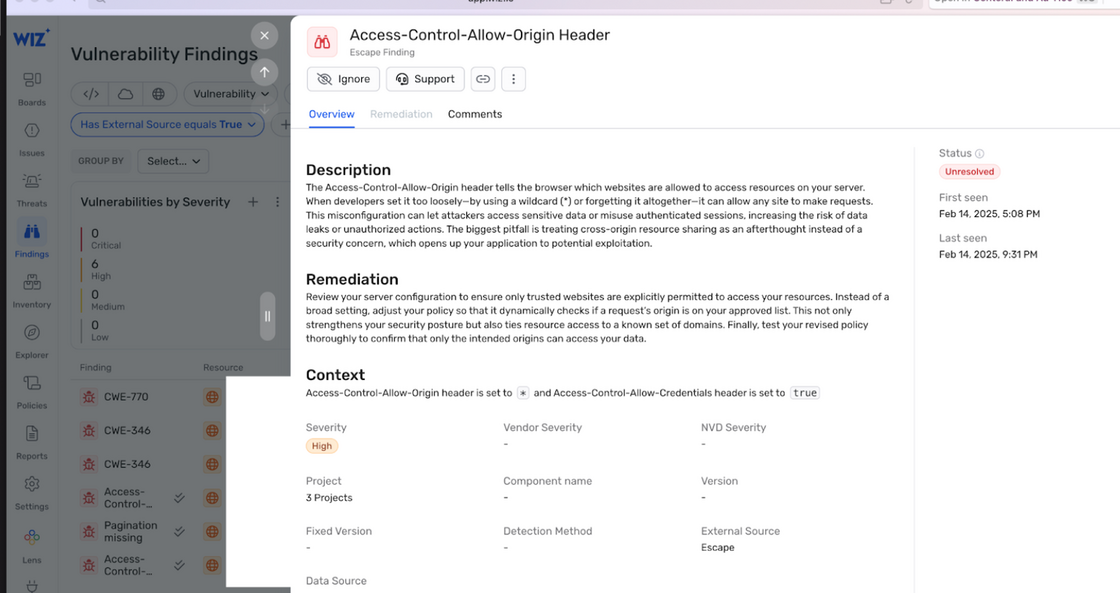
- All the vulnerabilities, exposed secrets, findings, and remediations are fed back into the Wiz using DAST & ASM Vulnerability Findings enrichment and Escape's workflows, merging both infrastructure and application-level insights into a single, unified view:
Want to benefit from the integration?Learn here how to set it up.