#127 · New Compliance Frameworks, Standards, and Resources Support
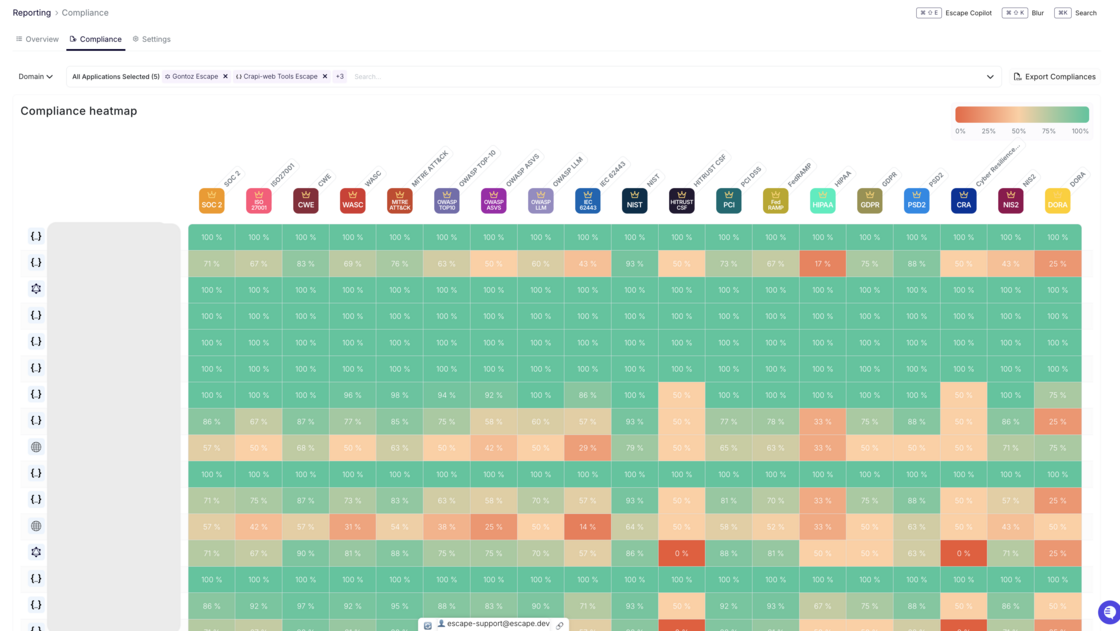
We are excited to announce the addition of 7 new compliance frameworks, standards and resources to our platform! This update helps ensure you have even more options to meet various regulatory and security requirements - whether you’re based in the US or the EU or working internationally.
What's New?
We’ve added support for the following compliance frameworks and resources:
- OWASP ASVS - Application Security Verification Standard with requirements for secure development.
- WASC - Best-practice security standards for web application security.
- MITRE ATT&CK - A knowledge base of adversary tactics, techniques, and procedures (TTPs), helping you understand and defend against cyber threats.
- IEC 62443 - Industrial automation and control systems security standards.
- HITRUST CSF - A framework for regulatory compliance and risk management in healthcare and beyond.
- CRA - EU Cyber Resilience Act, establishing cybersecurity requirements for products with digital elements.
- DORA - Digital Operational Resilience Act, ensuring that financial entities can withstand ICT-related disruptions.
Important Notes:
Some of these frameworks are OFF by default to keep your matrix manageable. You can enable them manually from the Reporting Settings page.
A full list of supported compliance standards can be found here.
We hope this update helps streamline your compliance and security efforts. Happy securing!