Webhook Notifications Integration
Webhook notifications allow you to export vulnerability data to your own systems and services. Data is sent as JSON payloads to your specified endpoint.
Configure the URL in Your Workflow
Set the webhook URL directly in the workflow action. That's the setup: No separate integration configuration is required.
Configuration
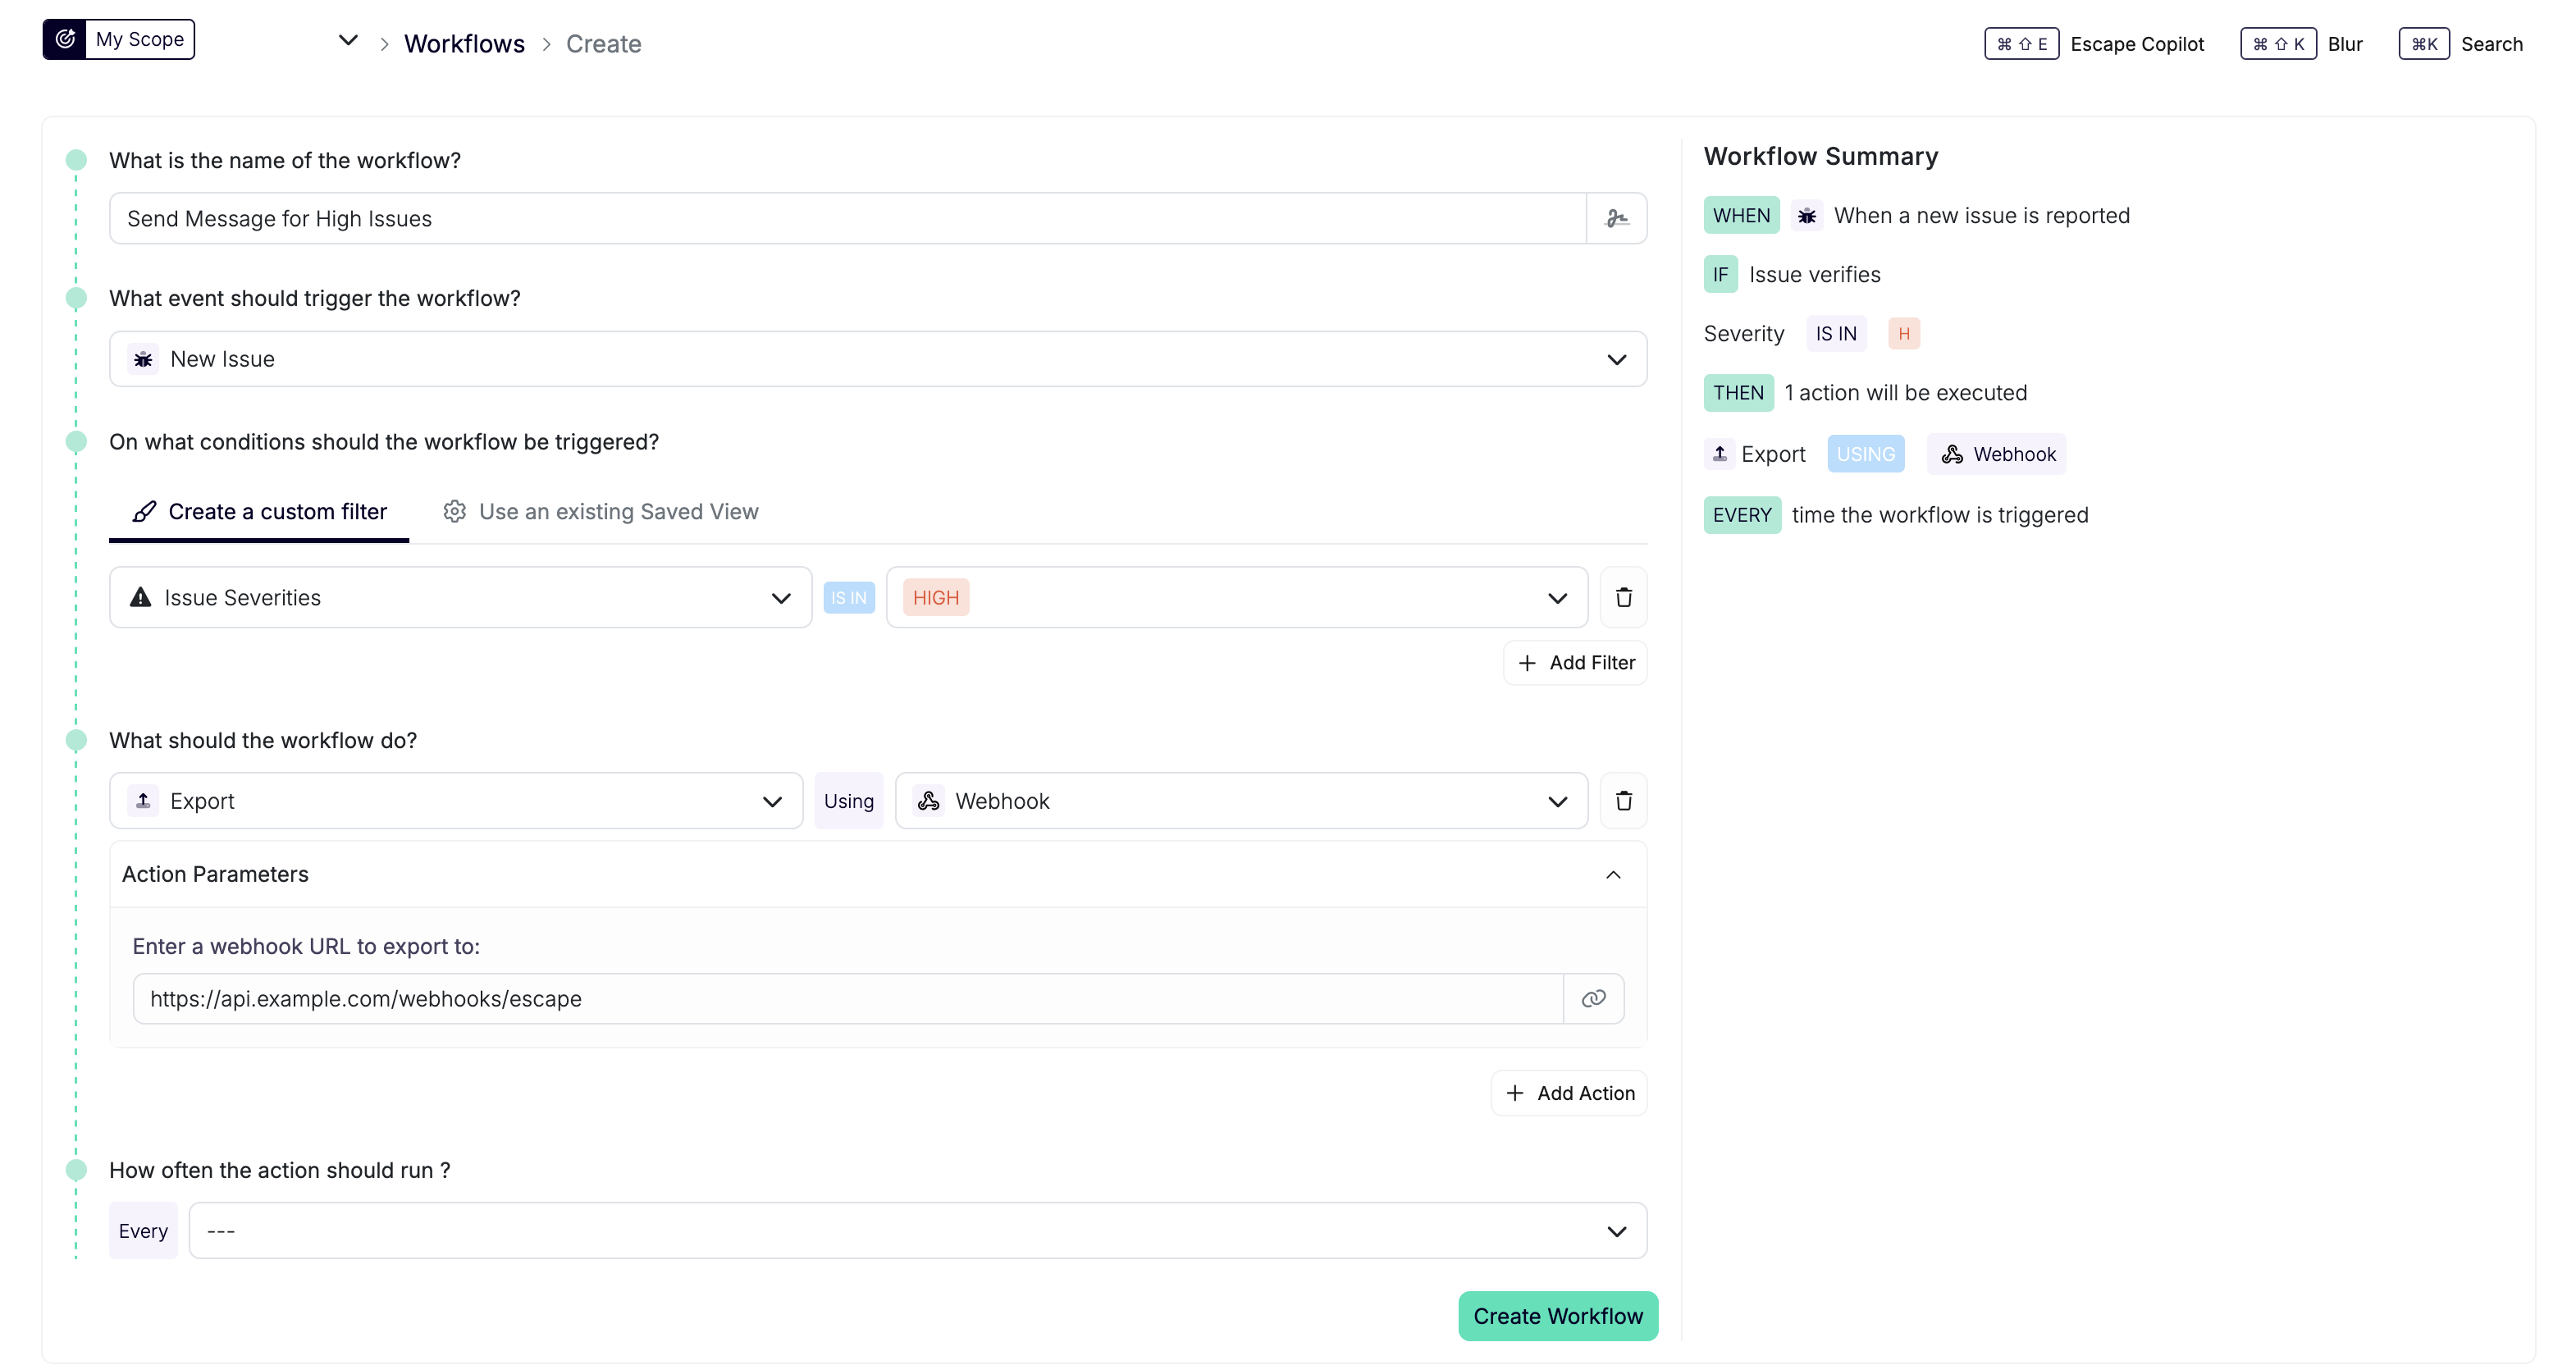
Webhook exports are configured as actions in workflows. When creating or editing a workflow:
- Go to Workflows → Create (or edit an existing workflow)
- In the Actions step, add an Export action
- Select Webhook as the integration type
- Enter your publicly reachable webhook URL where the data should be sent
- Add authentication or custom headers under Optional HTTP headers, if needed. They’re applied after the default
Content-Type: application/json, so you can override it. Header names are limited to 256 characters and values to 8192 characters.
The receiver must return a 2xx status for the export to succeed. Private and reserved destination addresses are rejected; webhook exports don’t route through a Private Location.
Firewall and Source IP
When a workflow runs, Escape sends an outbound POST from platform infrastructure to the URL you configured. Webhook exports bypass scan locations. If your receiver requires an IP allowlist, contact Escape support to confirm the current webhook egress addresses.
For the full firewall reference (scan IPs, platform callbacks, private locations, out-of-band testing), see Firewall configuration.
To verify the source IP on your side, trigger a test workflow and check the access logs on your webhook receiver.
Webhook Payload
When a workflow is triggered, Escape sends a POST request to your webhook URL with a JSON payload containing the resource data (issues, assets, scans, profiles, locations, and integrations) that matched the workflow conditions.
Root arrays are always present (possibly empty). Nested relation objects appear when available.
Escape supports two webhook payload shapes during a migration window:
| Setting |
Payload |
When to use |
| Off (default) |
Current: the payload shape your integration likely parses today |
Keep this until your consumer is updated |
| On |
Scoped: a smaller, stable field set |
Enable after updating your consumer |
Where to change it: Organization → General → Enable scoped webhook export payload (organization admins).
Update your webhook consumer before enabling the setting.
Integration Credentials in Default Payloads
Default integration exports include raw parameters, which can contain API tokens, PATs, or client secrets. Send them only to receivers trusted to handle those credentials. Use scoped payloads when the receiver doesn't need them.
Field-level reference for both shapes: Webhook payload reference.
Default Example Payload
{
  "issues": [
    {
      "id": "00000000-0000-0000-0000-000000000008",
      "name": "SQL Injection",
      "fullName": "SQL Injection - Critical",
      "severity": "HIGH",
      "category": "INJECTION",
      "status": "OPEN",
      "createdAt": "2024-01-15T10:30:00.000Z",
      "context": "The application is vulnerable to SQL injection...",
      "alertUid": "alert-123",
      "securityTestUid": "test-456",
      "assetId": "00000000-0000-0000-0000-000000000009",
      "asset": {
        "id": "00000000-0000-0000-0000-000000000009",
        "name": "https://api.example.com",
        "type": "REST",
        "class": "API_SERVICE",
        "uri": "asset://service/https://api.example.com",
        "createdAt": "2024-01-15T08:00:00.000Z",
        "service": {
          "id": "00000000-0000-0000-0000-000000000010",
          "url": "https://api.example.com",
          "type": "REST"
        },
        "tags": []
      },
      "targets": [
        {
          "id": "00000000-0000-0000-0000-000000000011",
          "targetUid": "target-789",
          "scanId": "00000000-0000-0000-0000-000000000012",
          "apiRoute": {
            "id": "00000000-0000-0000-0000-000000000013",
            "operation": "POST",
            "name": "/users",
            "coverage": "OK"
          }
        }
      ],
      "events": [],
      "scan": {
        "id": "00000000-0000-0000-0000-000000000012",
        "status": "FINISHED",
        "kind": "ASM_REST",
        "createdAt": "2024-01-15T09:00:00.000Z",
        "updatedAt": "2024-01-15T09:45:00.000Z",
        "applicationId": "00000000-0000-0000-0000-000000000014",
        "application": {
          "id": "00000000-0000-0000-0000-000000000014",
          "name": "My Application",
          "scannerKind": "ASM_REST",
          "type": "REST",
          "createdAt": "2024-01-15T07:00:00.000Z",
          "updatedAt": "2024-01-15T07:05:00.000Z"
        }
      },
      "application": {
        "id": "00000000-0000-0000-0000-000000000014",
        "name": "My Application",
        "scannerKind": "ASM_REST",
        "type": "REST",
        "createdAt": "2024-01-15T07:00:00.000Z",
        "updatedAt": "2024-01-15T07:05:00.000Z"
      }
    }
  ],
  "assets": [
    {
      "id": "00000000-0000-0000-0000-000000000015",
      "name": "https://app.example.com",
      "type": "WEBAPP",
      "class": "FRONTEND",
      "uri": "asset://frontend/https://app.example.com",
      "createdAt": "2024-01-15T08:00:00.000Z",
      "frontend": {
        "id": "00000000-0000-0000-0000-000000000020",
        "type": "WEBAPP",
        "url": "https://app.example.com",
        "ips": [
          "192.0.2.2"
        ],
        "regionCountryCodes": [
          "US"
        ],
        "tls": true
      },
      "scans": [],
      "events": []
    },
    {
      "id": "00000000-0000-0000-0000-000000000016",
      "name": "api.example.com",
      "type": "DNS",
      "class": "HOST",
      "uri": "asset://host/api.example.com",
      "createdAt": "2024-01-15T08:00:00.000Z",
      "host": {
        "id": "00000000-0000-0000-0000-000000000021",
        "type": "DNS",
        "address": "api.example.com",
        "ips": [
          "192.0.2.1"
        ],
        "regionCountryCodes": [
          "US"
        ],
        "records": [
          {
            "id": "00000000-0000-0000-0000-000000000019",
            "type": "A",
            "value": "192.0.2.1"
          }
        ],
        "ports": [
          {
            "port": 443,
            "protocols": [
              "HTTPS"
            ]
          }
        ]
      },
      "scans": [],
      "events": []
    },
    {
      "id": "00000000-0000-0000-0000-000000000017",
      "name": "escape/product",
      "type": "GITHUB_REPOSITORY",
      "class": "REPOSITORY",
      "uri": "asset://repository/github.com/escape/product",
      "createdAt": "2024-01-15T08:00:00.000Z",
      "repository": {
        "id": "00000000-0000-0000-0000-000000000022",
        "type": "GITHUB_REPOSITORY",
        "url": "https://github.com/escape/product",
        "visibility": "PRIVATE"
      },
      "scans": [],
      "events": []
    },
    {
      "id": "00000000-0000-0000-0000-000000000018",
      "name": "OpenAPI schema",
      "type": "OPENAPI",
      "class": "SCHEMA",
      "uri": "asset://schema/openapi/https://api.example.com/openapi.json",
      "createdAt": "2024-01-15T08:00:00.000Z",
      "schema": {
        "id": "00000000-0000-0000-0000-000000000023",
        "type": "OPENAPI",
        "key": "https://api.example.com/openapi.json",
        "s3Key": "schemas/aa/bb/openapi.json"
      },
      "scans": [],
      "events": []
    }
  ],
  "scans": [
    {
      "id": "00000000-0000-0000-0000-000000000024",
      "status": "FINISHED",
      "kind": "ASM_REST",
      "createdAt": "2024-01-15T09:00:00.000Z",
      "updatedAt": "2024-01-15T10:00:00.000Z",
      "applicationId": "00000000-0000-0000-0000-000000000026",
      "application": {
        "id": "00000000-0000-0000-0000-000000000026",
        "name": "My Application",
        "scannerKind": "ASM_REST",
        "type": "REST",
        "createdAt": "2024-01-15T07:00:00.000Z",
        "updatedAt": "2024-01-15T07:05:00.000Z"
      }
    }
  ],
  "profiles": [
    {
      "id": "00000000-0000-0000-0000-000000000027",
      "name": "My Application",
      "scannerKind": "ASM_REST",
      "type": "REST",
      "createdAt": "2024-01-15T07:00:00.000Z",
      "updatedAt": "2024-01-15T07:00:00.000Z"
    }
  ],
  "locations": [
    {
      "id": "00000000-0000-0000-0000-000000000001",
      "name": "US East",
      "type": "PRIVATE",
      "target": "proxy.example.com",
      "ip": "192.0.2.1",
      "region": "UnitedStates",
      "enabled": true,
      "createdAt": "2024-01-15T06:00:00.000Z"
    }
  ],
  "integrations": [
    {
      "id": "00000000-0000-0000-0000-000000000002",
      "name": "GitHub Org Integration",
      "kind": "GITHUB_API_KEY",
      "valid": true,
      "createdAt": "2024-01-15T06:00:00.000Z",
      "updatedAt": "2024-01-15T06:00:00.000Z"
    }
  ]
}
Payload Structure
Fields marked optional may be absent or null depending on the resource and trigger context.
Root Object
| Field |
Type |
Description |
issues |
array<Issue> |
Array of issue objects that matched the workflow conditions. Empty array if no issues matched. |
assets |
array<Asset> |
Array of asset objects that matched the workflow conditions. Empty array if no assets matched. |
scans |
array<ResourceScan> |
Array of scan objects that matched the workflow conditions. Empty array if no scans matched. |
profiles |
array<Application> |
Array of application/profile objects that matched the workflow conditions. Empty array if no profiles matched. |
locations |
array<Proxy> |
Array of proxy/location objects that matched the workflow conditions. Empty array if no locations matched. |
integrations |
array<Integration> |
Array of integration objects that matched the workflow conditions. Empty array if no integration item is included. |
Issue Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the issue |
name |
string |
Short name of the issue |
fullName |
string |
Full name of the issue, including risk information |
severity |
string (enum) |
Severity level: CRITICAL, HIGH, MEDIUM, LOW, INFO |
category |
string (enum) |
Issue category (for example, INJECTION, ACCESS_CONTROL, SCHEMA) |
status |
string (enum) |
Issue status: OPEN, RESOLVED, MANUAL_REVIEW, IGNORED, FALSE_POSITIVE |
createdAt |
string (ISO 8601) |
Timestamp when the issue was created |
context |
string |
Description and context of the issue |
alertUid |
string |
Unique identifier for the alert |
securityTestUid |
string |
Unique identifier for the security test |
assetId |
string (UUID) |
ID of the asset associated with this issue |
asset |
object |
Asset details with tags, service, frontend, host, and cloudComponent (see Nested Issue Asset below) |
targets |
array<object> |
Array of scan targets where this issue was found |
events |
array<object> |
Array of events related to this issue |
scan |
object (optional) |
Scan object if the issue is associated with a specific scan |
application |
object (optional) |
Application object if the issue is associated with a scan |
Nested Issue Asset
The issue’s asset contains asset details plus tags, service, frontend, host, and cloudComponent. Missing nullable relations are null. It doesn’t include root asset relations such as schema, repository, scans, or events.
Asset Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the asset |
name |
string |
Display name of the asset |
type |
string (enum) |
Asset type (for example, REST, WEBAPP, DNS, GITHUB_REPOSITORY, OPENAPI) |
class |
string (enum) |
Asset class (for example, API_SERVICE, FRONTEND, HOST, REPOSITORY, SCHEMA) |
uri |
string |
Uniform Resource Identifier uniquely identifying the asset |
createdAt |
string (ISO 8601) |
Timestamp when the asset was first discovered |
service |
object (optional) |
Service details if the asset is a service |
frontend |
object (optional) |
Frontend details if the asset is a frontend |
host |
object (optional) |
Host details if the asset is a host |
repository |
object (optional) |
Repository details if the asset is a repository |
schema |
object (optional) |
Schema associated with the asset |
scans |
array<object> |
Array of scans that discovered or updated this asset |
events |
array<object> |
Array of events related to this asset |
tags |
array<object> (optional) |
Array of tags associated with the asset |
ResourceScan Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the scan |
status |
string (enum) |
Scan status: STARTING, RUNNING, FINISHED, FAILED, CANCELED |
kind |
string (enum) |
Type of scan (for example, FRONTEND_DAST, BLST_REST, ASM_REST) |
createdAt |
string (ISO 8601) |
Timestamp when the scan was created |
updatedAt |
string (ISO 8601) |
Timestamp when the scan was last updated |
finishedAt |
string (ISO 8601, optional) |
Timestamp when the scan finished |
progressRatio |
number |
Progress ratio from 0 to 1 |
applicationId |
string (UUID) |
ID of the application being scanned |
application |
Application (object) |
Complete application object with nested relations |
Application Object (Profile)
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the application |
name |
string |
Name of the application |
scannerKind |
string (enum) |
Type of scanner used (for example, FRONTEND_DAST, BLST_REST) |
type |
string (enum) |
API type: REST, GRAPHQL, GRPC |
createdAt |
string (ISO 8601) |
Timestamp when the application was created |
updatedAt |
string (ISO 8601) |
Timestamp when the application was last updated |
Proxy Object (Location)
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the proxy/location |
name |
string |
Display name of the location |
type |
string (enum) |
Proxy type: ESCAPE, PRIVATE |
target |
string |
Target URL or hostname of the proxy |
ip |
string (optional) |
IP address of the proxy |
region |
string (optional) |
Geographic region of the proxy |
enabled |
boolean |
Whether the proxy is currently enabled |
createdAt |
string (ISO 8601) |
Timestamp when the proxy was created |
Integration Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the integration |
name |
string |
Integration display name |
kind |
string (enum) |
Integration kind (for example, GITHUB_API_KEY, WEBHOOK) |
valid |
boolean |
Whether the integration is currently considered valid |
parameters |
object |
Raw integration configuration, potentially including credentials |
createdAt |
string (ISO 8601) |
Timestamp when the integration was created |
updatedAt |
string (ISO 8601) |
Timestamp when the integration was last updated |
ResourceScanTarget Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the target |
targetUid |
string |
Unique identifier used to deduplicate targets |
scanId |
string (UUID, optional) |
ID of the scan that found this target |
apiRoute |
ResourceScanTargetAPIRoute (object, optional) |
API route details if the target is an API route |
codeFile |
ResourceScanTargetCodeFile (object, optional) |
Code file details if the target is a code file |
graphqlResolver |
ResourceScanTargetGraphQLResolver (object, optional) |
GraphQL resolver details if the target is a GraphQL resolver |
webPage |
ResourceScanTargetWebPage (object, optional) |
Web page details if the target is a web page |
webCrawledUrl |
ResourceScanTargetWebCrawledUrl (object, optional) |
Web crawled URL details if the target is a crawled URL |
AssetService Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the service |
url |
string |
Base URL of the service |
type |
string (enum) |
Service type: REST, GRAPHQL, GRPC, WEBSOCKET, MCP |
framework |
string (enum, optional) |
Framework used by the service |
authProtocol |
string (enum, optional) |
Authentication protocol used |
authTechnology |
string (enum, optional) |
Authentication technology used |
cloudProvider |
string (enum, optional) |
Cloud provider hosting the service |
environment |
string (enum, optional) |
Environment: PRODUCTION, STAGING, DEVELOPMENT |
AssetFrontend Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the frontend |
type |
string (enum) |
Frontend type (currently WEBAPP) |
url |
string |
Frontend URL |
framework |
string (enum, optional) |
Frontend framework |
authProtocol |
string (enum, optional) |
Authentication protocol |
authTechnology |
string (enum, optional) |
Authentication technology |
cloudProvider |
string (enum, optional) |
Cloud provider |
environment |
string (enum, optional) |
Environment |
ips |
array<string> |
Resolved IPs for the frontend |
regionCountryCodes |
array<string> |
Country codes where the frontend is observed |
tls |
boolean |
Whether TLS is enabled |
AssetHost Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the host |
type |
string (enum) |
Host type: DNS, IPV4, IPV6 |
address |
string |
Main host address |
ips |
array<string> |
Resolved IP addresses |
regionCountryCodes |
array<string> |
Country codes where the host is observed |
ports |
array<AssetHostPort> |
Open ports and protocols |
records |
array<AssetHostRecord> |
DNS records |
AssetHostPort Object
| Field |
Type |
Description |
port |
number |
Network port |
protocols |
array<string> |
Detected protocols (for example, HTTP, HTTPS) |
AssetHostRecord Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the DNS record |
type |
string |
Record type (for example, A, CNAME, MX) |
value |
string |
Record value |
AssetRepository Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the repository |
type |
string (enum) |
Repository type: GITHUB_REPOSITORY, GITLAB_REPOSITORY, BITBUCKET_REPOSITORY |
url |
string |
Repository URL |
name |
string (optional) |
Repository name |
visibility |
string (enum, optional) |
Visibility: PUBLIC, PRIVATE, INTERNAL |
archived |
boolean (optional) |
Whether the repository is archived |
lastCommitSha |
string (optional) |
Last commit SHA |
lastCommitDate |
string (ISO 8601, optional) |
Last commit date |
AssetSchema Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the schema |
type |
string (enum) |
Schema type: OPENAPI, GRAPHQL_SCHEMA, POSTMAN_COLLECTION, and similar |
key |
string |
Stable schema identifier (URL or generated key) |
s3Key |
string |
Storage key for the schema artifact |
source |
string (enum, optional) |
Schema source: UPLOADED, GENERATED, FOUND |
ResourceScanTargetAPIRoute Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the API route |
operation |
string (enum) |
HTTP method: GET, POST, PUT, DELETE, PATCH, and similar |
name |
string |
Path or route name |
parameters |
object (optional) |
JSON object containing parameter definitions |
returnType |
string (optional) |
Return type of the route |
coverage |
string (enum, optional) |
Coverage status of the route |
ResourceScanTargetCodeFile Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the code file |
language |
string |
Programming language of the file |
path |
string |
File path relative to the repository root |
ResourceScanTargetGraphQLResolver Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the GraphQL resolver |
parent |
string |
Parent type name |
name |
string |
Resolver name |
parameters |
object (optional) |
JSON object containing parameter definitions |
returnType |
string (optional) |
Return type of the resolver |
ResourceScanTargetWebPage Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the web page |
url |
string |
URL of the web page |
visits |
number |
Number of times this page was visited during the scan |
ResourceScanTargetWebCrawledUrl Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the crawled URL |
url |
string |
URL that was crawled |
ResourceScanEvent Object
| Field |
Type |
Description |
id |
string (UUID) |
Unique identifier of the event |
title |
string |
Title of the event |
description |
string |
Description of the event |
level |
string (enum) |
Event level: DEBUG, INFO, WARNING, ERROR |
stage |
string (enum) |
Event stage: CONFIGURATION, EXECUTION, AGENT_REASONING, AGENT_ACTION |
createdAt |
string (ISO 8601) |
Timestamp when the event was created |
attachments |
array<object> |
Array of attachments, such as exchanges, snippets, or screenshots |
Note
The example above is the default (current) payload. For the scoped example and field catalog, see Webhook payload reference. Consumers should ignore unknown fields for forward compatibility.