#178 · AI Pentest profiles now ship with default scope restrictions
Escape's AI Pentesting runs a multi-agent harness that explores your app the way an attacker would. Scope restrictions are how you tell it where not to go. Until now, that list started empty on every new profile, which meant configuring it before the first run, or letting an autonomous agent loose on your app with no guardrails at all.
Now it comes pre-filled.
What's new
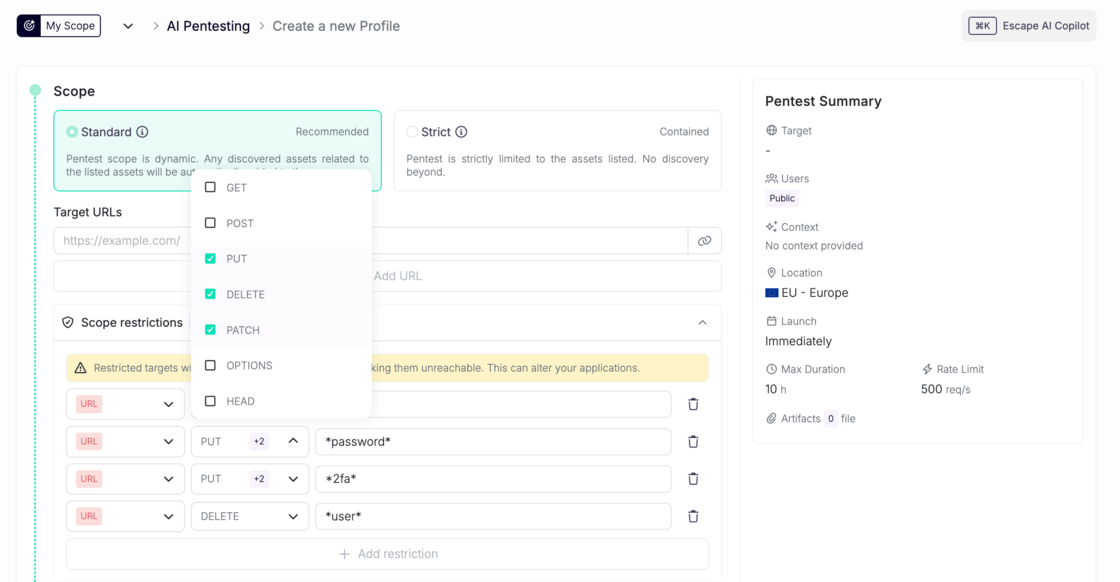
Every new AI Pentest profile now starts with a curated blocklist of URL patterns, covering destructive and sensitive routes like delete, admin, and auth endpoints. It's the same default blocklist behavior DAST profiles have had, now applied to AI Pentesting.
Why it matters
- A sensible baseline with no configuration. Create a profile, run it, and the obvious foot-guns are already out of scope.
- Lower risk of accidental damage during a run. Autonomous agents are good at finding paths you didn't think to exclude, which is the point of them and also the problem.
And of course, you can add, remove, or replace patterns as you learn your own app's shape.
Applies to all newly created AI Pentest profiles. Existing profiles are unchanged.