#171 · ASM Login and CAPTCHA Detection: See Auth Friction on Every Web App
Availability: General Availability
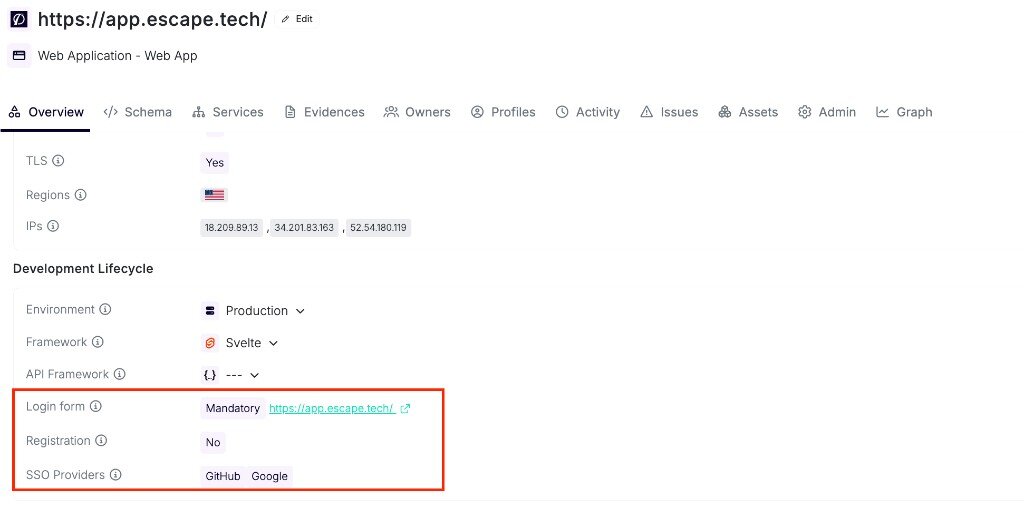
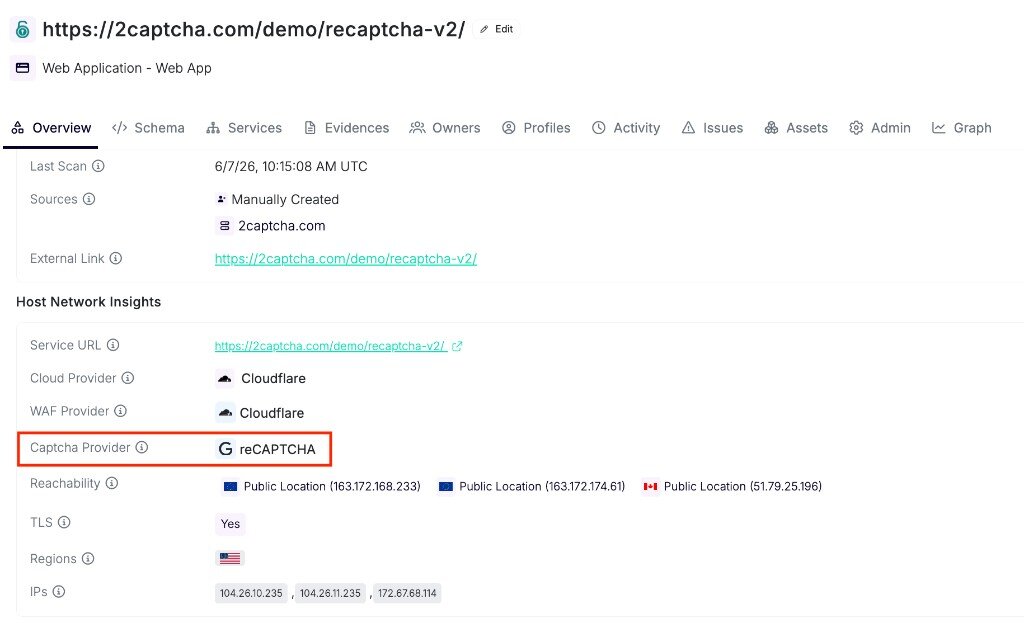
Every ASM web app scan now fingerprints the login surface before you touch scan profiles. You get the login requirement, login page URL, registration path, SSO providers, auth protocol, auth technology, and CAPTCHA provider on each asset. AppSec teams told us they need this context upfront: which apps gate sign-in with MFA or CAPTCHA, and where SSO redirects land, before they configure authenticated DAST or plan allowlists.
What's new:
-
Login page discovery: an agent browses each web app and records whether login is mandatory, optional, or absent, plus the login page URL and detected SSO providers.
-
Auth fingerprinting: HTTP probing and redirect analysis classify auth protocol and technology (OAuth, OIDC, Auth0, Cognito, and similar) on web apps, REST APIs, and GraphQL APIs.
-
CAPTCHA provider detection: dual fingerprinting via HTTP technology signatures and browser rendering flags reCAPTCHA, hCaptcha, Cloudflare Turnstile, and other providers on each frontend.
-
Filters: filter web apps by CAPTCHA provider and review login and auth fields from the asset side panel.
Asset Management documentation →
Questions?
Have a question? Reach out on your dedicated support channel, or email us at support@escape.tech.