#175 · AWS Integration IAM Roles: Connect Accounts Without Long-Lived Access Keys
Availability: General Availability
Escape connects to your AWS accounts through IAM role assumption and an External ID. You grant access with a role trust policy instead of storing long-lived access keys, the same short-lived credential pattern you use for other enterprise SaaS integrations at scale. Add the new AWS integration type from the integrations page; the legacy access-key path stays available.
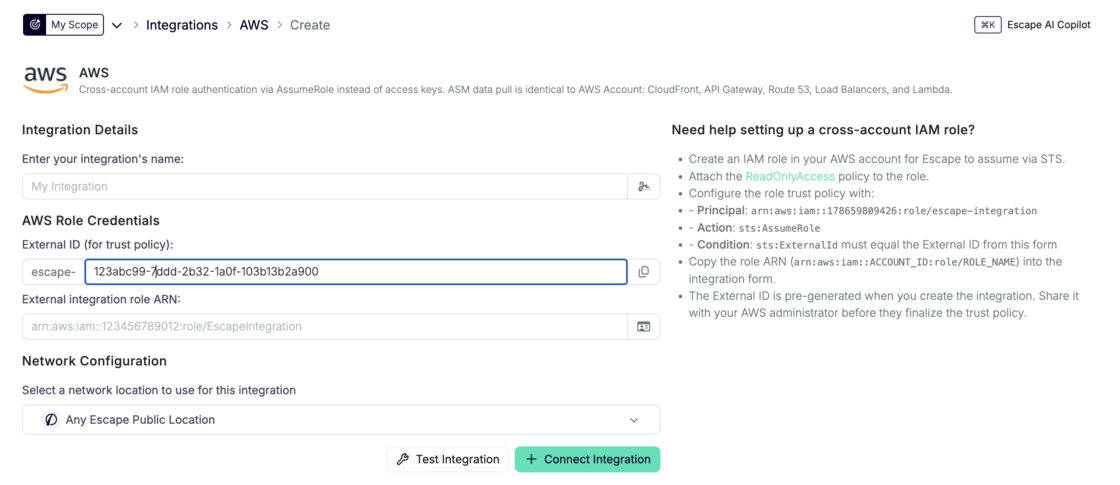
What's new:
- AWS integration type: Add an integration that authenticates through STS AssumeRole with an External ID instead of static credentials.
- No long-lived keys: Grant access through a role trust policy instead of static credentials stored in Escape.
- Legacy path preserved: The existing AWS_ACCOUNT integration (access keys) remains for backward compatibility and is marked as legacy in the UI.
AWS integration documentation →
Questions?
Have a question? Reach out on your dedicated support channel, or email us at support@escape.tech.