#174 · Custom session login in AI Pentesting: paste your cookie, headers, localstorage, we handle the rest
Getting past custom authentication is where most automated testing stops short. Sometimes a hardcoded value is the only way through. Now it's one line of text.
You can now hand the Escape's AI Pentesting agent a session directly. Paste your cookie, headers, or local storage values into the authentication instructions as plain text, and the agent starts the run already authenticated.
What's new
In the user authentication instructions, write your session details as plain text. For example:
Use the session cookie session=abc123 for https://app.customer.com. It's already valid, no need to log in.
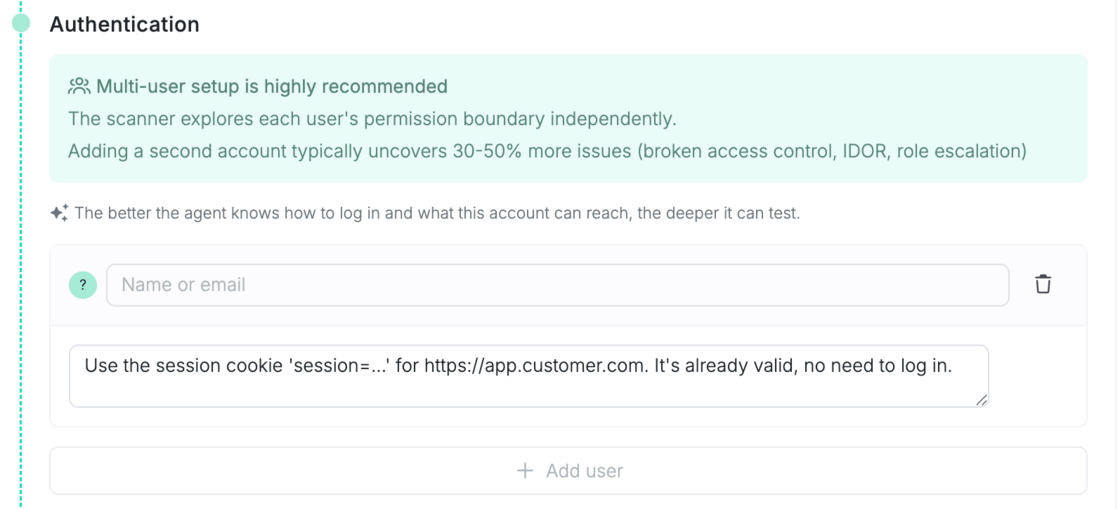
Escape extracts the cookie, along with any request headers or local storage values you include, and injects them into the agent's browser before the run starts. The agent lands already authenticated.
This works per user, so each role you configure in the scan setup flow can carry its own session. Available in both AI Pentesting and pentest target validation, so behavior is consistent across the product. Describing a login flow still works and stays the default.
Why it matters
- Works for the hard cases: SSO, MFA, custom tracing header. Sometimes a hardcoded value is required to bypass things.
- No setup overhead. It's the existing instructions field, in plain text. No new form, no config, no onboarding change.
Security & safety
This handles live credentials, so we were deliberate:
- Extracted secrets are not sent to asset or reporting events. Session values don't appear in logs or reports.
- A dedicated extractor model parses only what you explicitly write. It never invents credentials.