#183 · wp2shell detection is live (CVE-2026-63030, CVE-2026-60137)
Availability: General Availability
wp2shell is an unauthenticated RCE chain in WordPress core. A REST batch route-confusion flaw (CVE-2026-63030) skips authentication and feeds a SQL injection in WP_Query (CVE-2026-60137). No plugins, no login. It affects WordPress 6.9.0 to 6.9.4 and 7.0.0 to 7.0.1, is already being exploited in the wild, and is fixed in 6.9.5 and 7.0.2.
Escape now detects it across DAST and AI Pentesting. DAST confirms the injection with a time-based oracle instead of guessing from a version string, and AI Pentesting walks the full chain and returns proof of exploitation.
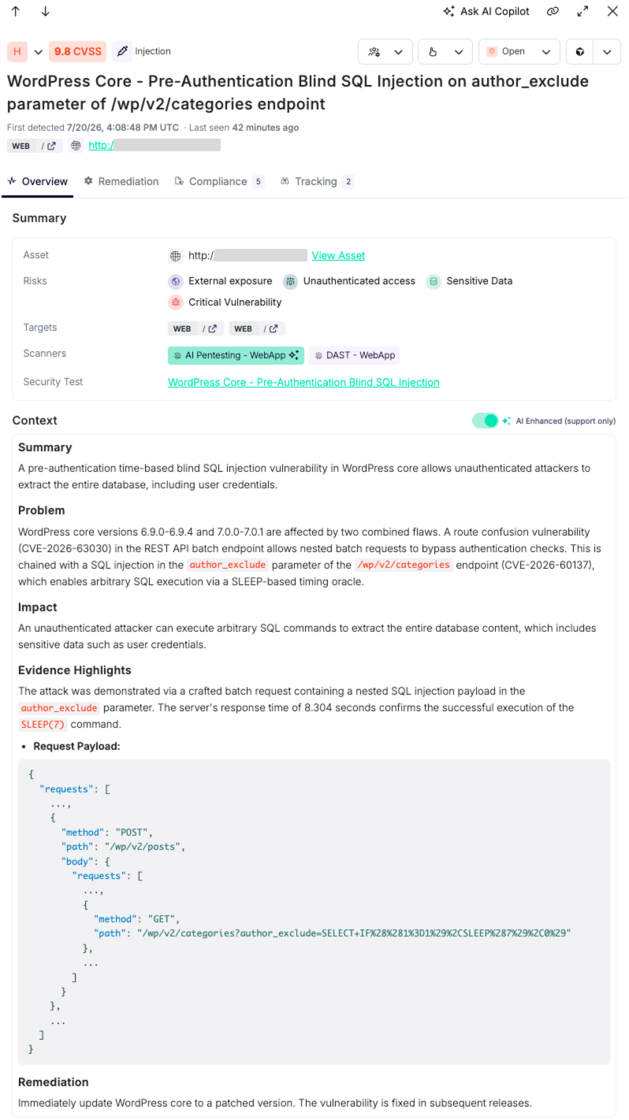
Recommended action: connect to your Escape account to verify whether you've been affected, update to 6.9.5 or 7.0.2, and confirm the auto-update actually applied.
We proactively reach out to our current customers who might have been affected by this issue.
See your exposure in one view
- Open All Issues.
- Search for "WordPress Core - Pre-Authentication".
- Save as a new view.
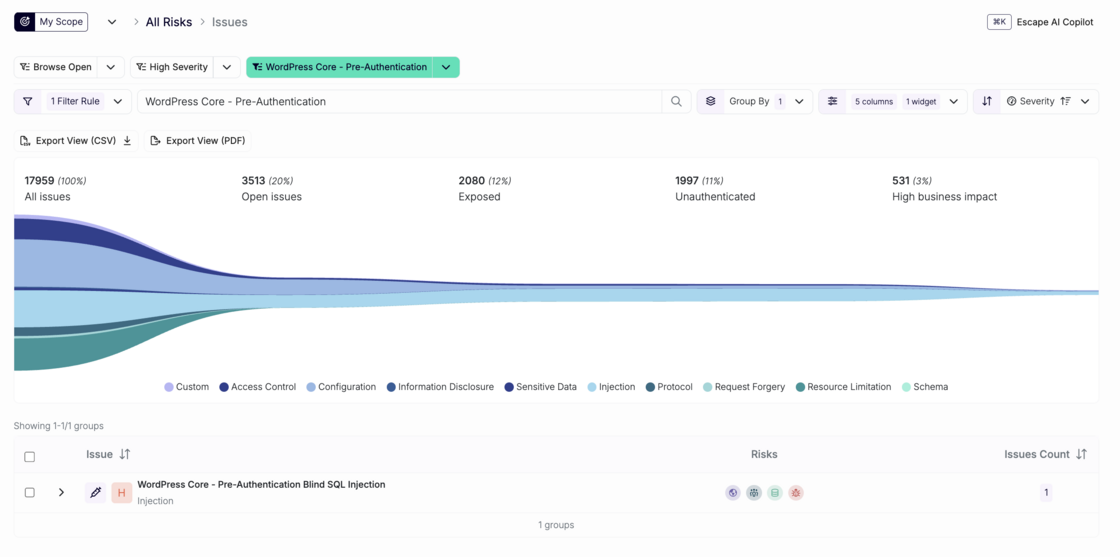
You get a live view of every affected asset, with the exposed and unauthenticated counts broken out for triage.
Questions?
Have a question? Reach out on your dedicated support channel, or email us at support@escape.tech.