#185 · Whitebox pentesting is now available in Escape's AI Pentesting
Every yearly pentest opens the same way: the first hours go to mapping what you already know. Cascade can now start from the code instead.
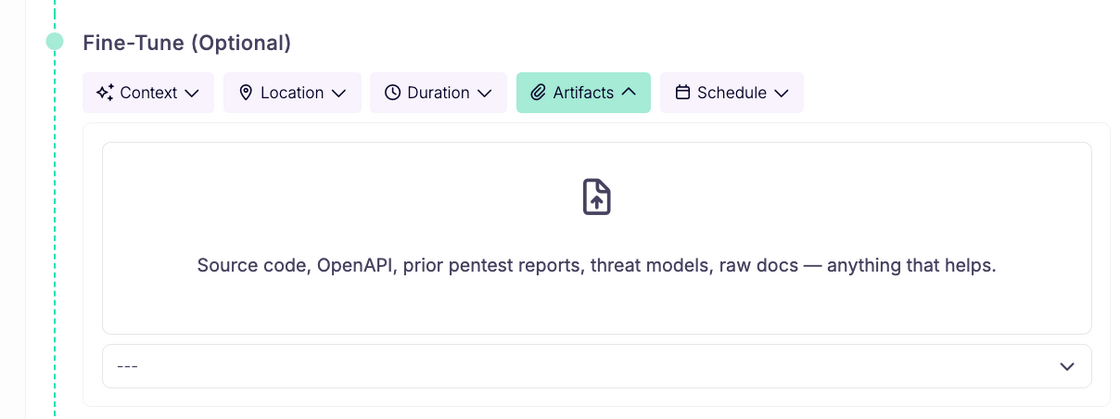
Attach your repository as a .zip under Fine-Tune (Optional) then Artifacts when you launch a pentest.
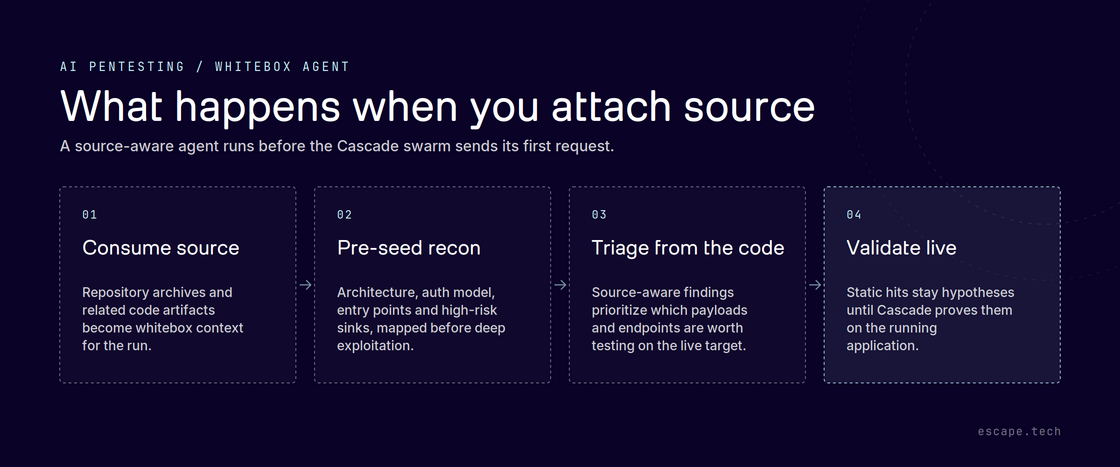
The whitebox agent reads it before the swarm sends its first request, mapping architecture, auth model, entry points and high-risk sinks, and every later agent inherits that context. Findings can now point at the exact file and function behind a vulnerability, with the code attached as evidence.
Static hits stay hypotheses. Source-derived leads are still validated against the running application before anything reaches your report, so report quality is unchanged.
Across our internal benchmarks, detection improves by 32% on average.
Archives get a larger ceiling, 200 MB per archive and 250 MB per run, and are routed to the whitebox agent automatically with no toggle to set. Secrets found in code are never reported as findings or persisted un-redacted, and only reusable architecture carries between scans.
Available on demand. You can learn more about Cascade's whitebox agent in our documentation.