#168 · Introducing Cascade: Penetration Testing That Becomes an Expert in Your Business
Availability: General Availability
Cascade is Escape's multi-agent AI pentest engine. It starts every engagement with what the platform already knows about your attack surface: APIs, web apps, schemas, tech stack, and scope from ASM and DAST. You're not pointing a stranger at a URL. You're running an assessment that compounds context across releases and gets sharper about how your business actually works.
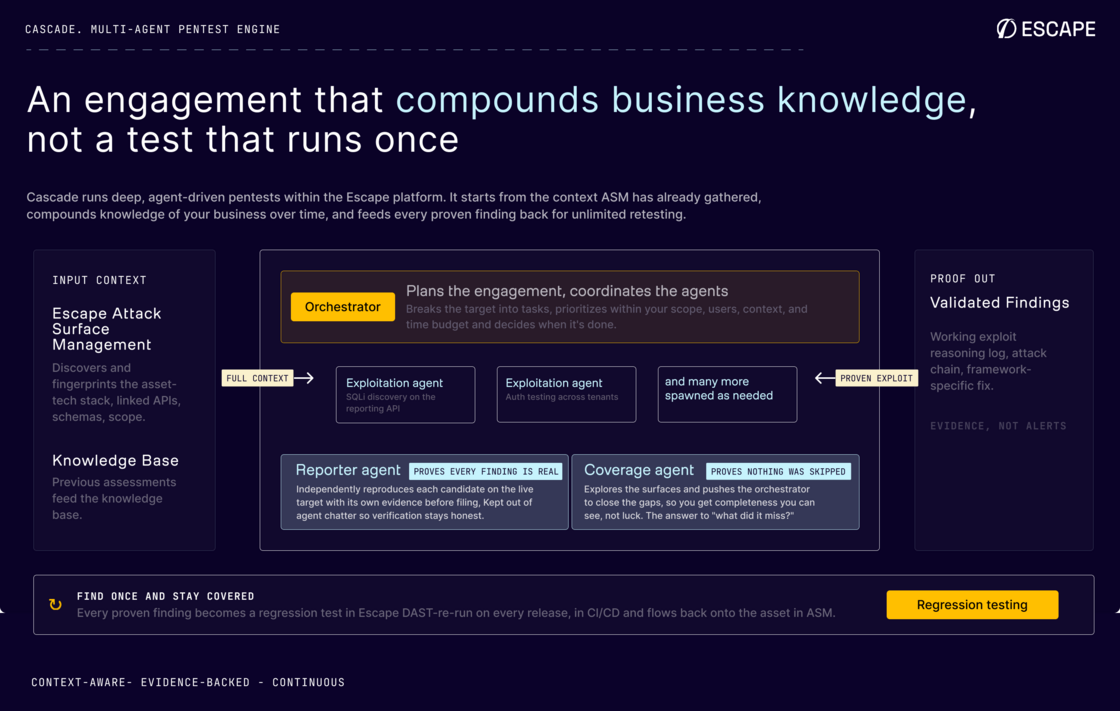 Cascade starts from ASM context, coordinates a multi-agent swarm, and ships every finding with proof.
What's new:
- Multi-agent swarm: An orchestrator plans the engagement and spawns focused exploitation agents on demand. A coverage agent closes gaps. A reporter independently reproduces every candidate before it's filed.
- Proof of exploit: Every finding ships with the attack chain, request sequence, screenshots where relevant, and framework-specific remediation. Unproven candidates don't pollute your queue.
- Auditable scope: Discovery maps your full configured scope before exploitation. You see exactly which endpoints, pages, and assets were assessed.
AI Pentesting documentation →\ Introducing Cascade on the Escape blog →
Questions?
Have a question? Reach out on your dedicated support channel, or email us at support@escape.tech.