#173 · ASM Technology Detection: Map Every Asset to Known CVEs
Availability: General Availability
Escape ASM fingerprints the software on each asset: packages, frameworks, and infrastructure components, with versions when the stack exposes them. You get a live technology inventory across web apps, APIs, and connected repositories, matched to known CVEs so you trace a vulnerable dependency to every asset that runs it.
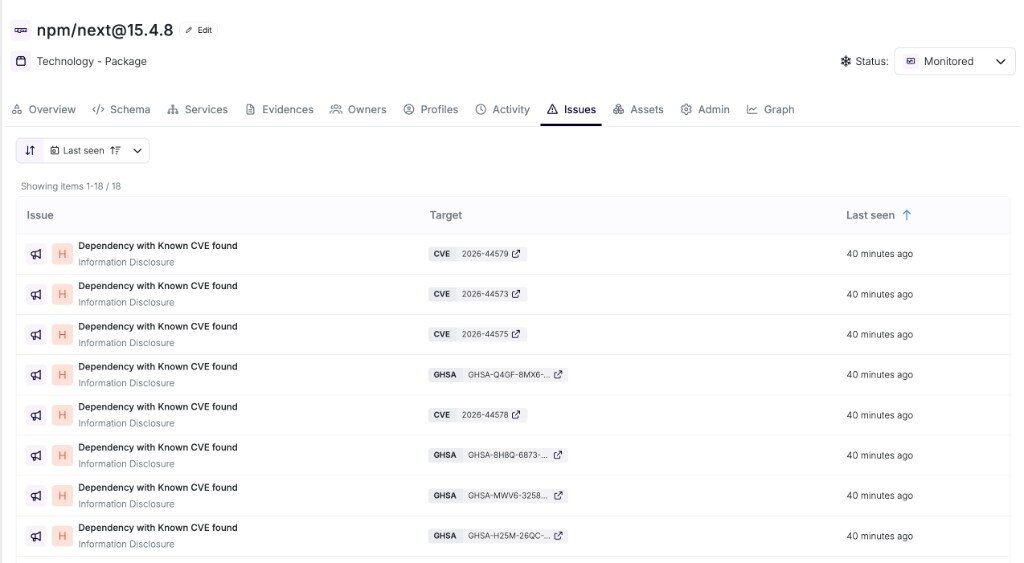 Known CVEs matched to a detected package version.
What's new:
- Multi-source fingerprinting: HTTP response analysis, source maps, stack traces, protocol-level signals, and repository manifest parsing identify packages and deployed software without installing agents on your infrastructure.
- Packages and software: libraries from npm, PyPI, and other ecosystems sit alongside web servers, CMS platforms, and reverse proxies, each linked back to the parent asset.
- Version-aware CVE matching: versioned technologies match against affected ranges at high confidence; versionless detections still map through standard product identifiers at adjusted confidence.
- Actionable findings: matches become Vulnerable Dependency Detected issues with severity, affected versions, fix version when available, and advisory links.
Technology Detection documentation →
Questions?
Have a question? Reach out on your dedicated support channel, or email us at support@escape.tech.