#194 · Secrets Vault Integration: Credentials That Stay Current
Availability: General Availability
Your scan credentials now live in one place. Create a variable once, reference it as {{KEY}} in any profile, and rotate it without opening a single scan configuration. Point it at Azure Key Vault and Escape reads the current secret each time a scan starts, so a rotated password stops breaking your scans.
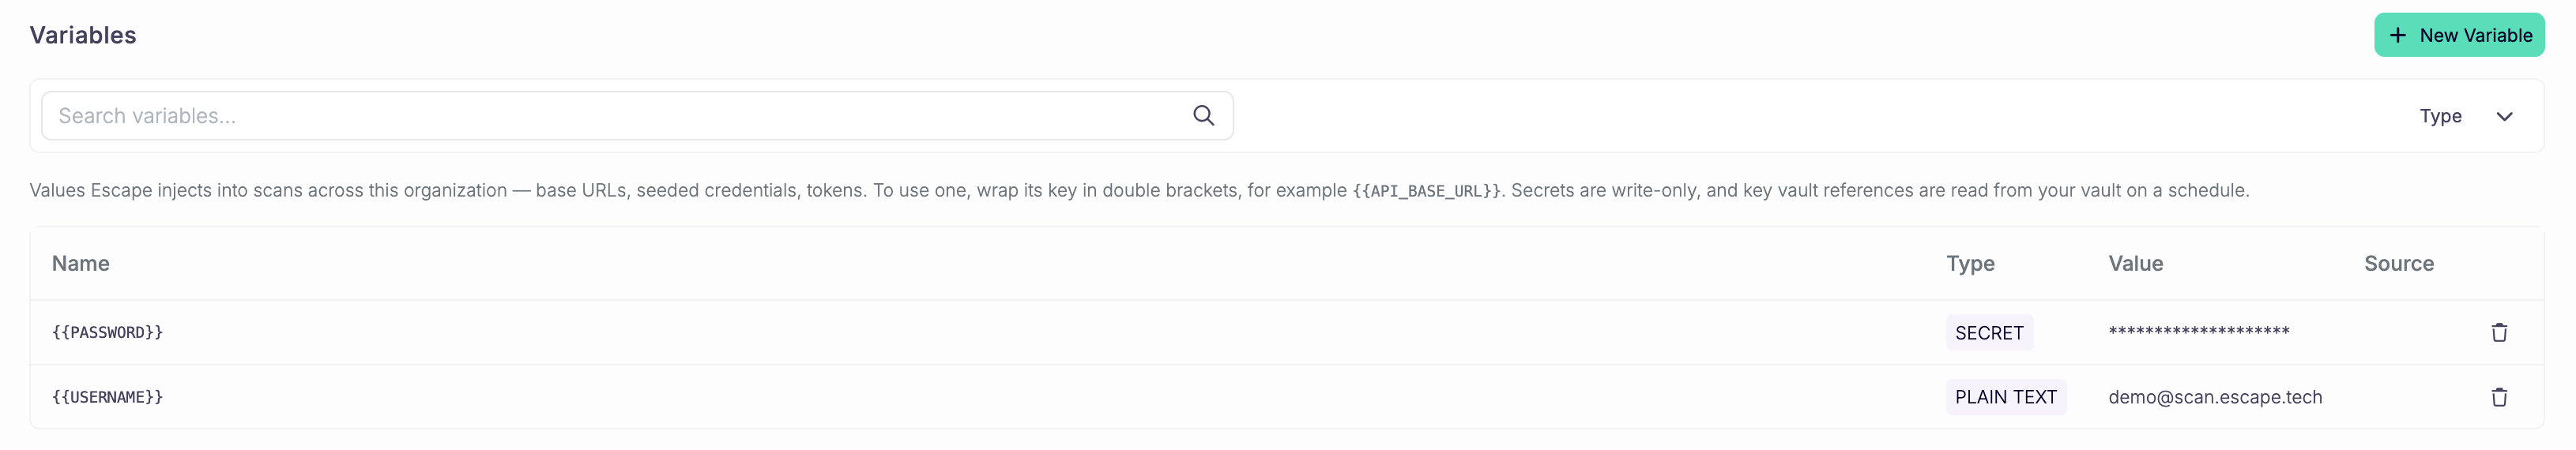 Organization Variables: one list for every value your scans share.
What's New
- Three variable types: Plain text stays readable. Secret is write-only after you save it. External is a reference to a secret that stays in your Azure Key Vault.
- Azure Key Vault: create an Azure Key Vault integration with a tenant ID, client ID, and client secret, then pick the vault and the secret name when you create an external variable.
- Redaction: in scan outputs, secret and external values of 8 characters or more are replaced with
[REDACTED: KEY]. - Audit trail: each scan that reads variables writes an audit log entry listing the keys it used.
- API:
/v3/vault-variableslists, creates, and deletes variables,POST /v3/vault-variables/{variableId}/rotaterotates one, andGET /v3/vaultslists linked vaults.
How It Works
Write {{KEY}} anywhere a string value appears in a profile's configuration: a username, a password, a header, a URL.
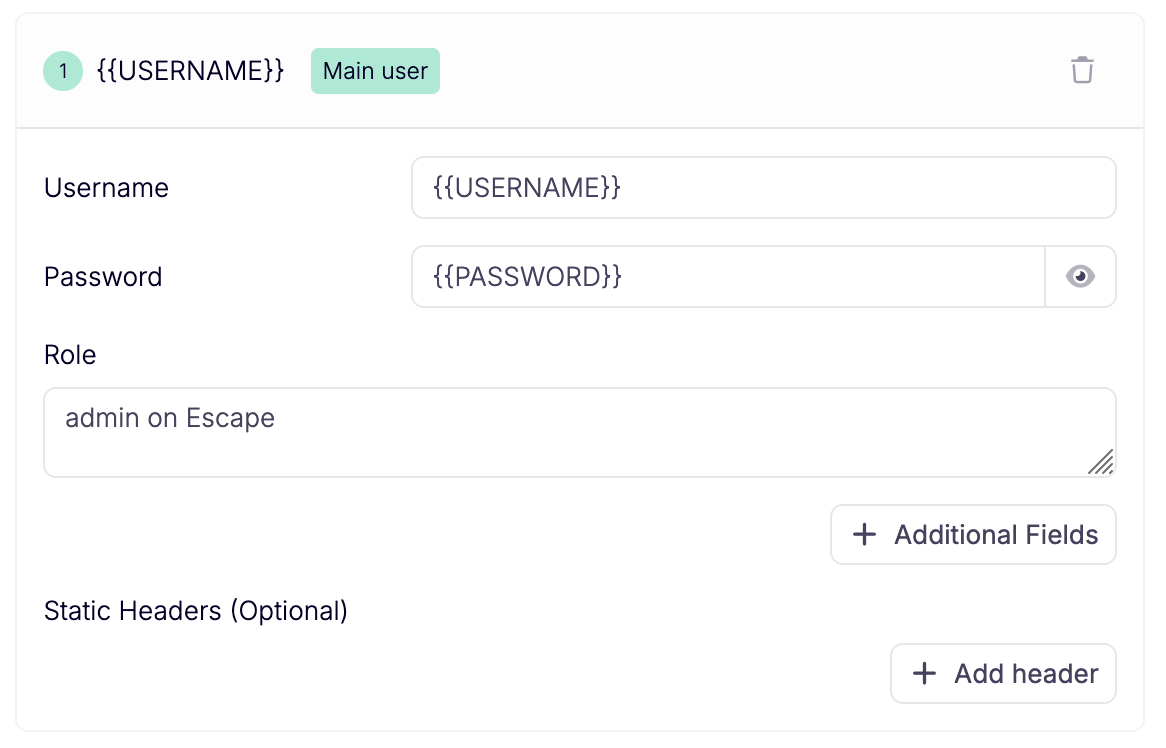 A profile user set to
{{USERNAME}} and {{PASSWORD}}.
When a scan starts, Escape resolves every referenced variable once and reuses those values for the whole run. External variables are read live from your vault at that moment. If Escape fails to read one (the secret was deleted or disabled, or access is refused), the scan fails at start instead of running without credentials.
Requirements and Limits
- Managing variables and linking vaults requires Manage Vault Variables or Admin through a global role binding.
- A key is
SCREAMING_SNAKE_CASE, starts with a letter, and holds up to 128 characters. - Azure Key Vault is the external vault supported today. The service principal needs Reader on the subscription and Key Vault Secrets User on each vault.
- Values are read once at scan start: a secret must stay valid for the full run.
- Plain text values and values shorter than 8 characters aren't redacted.
Variables Docs → Read the Announcement →
HashiCorp Vault is next.
Questions?
Have a question? Reach out on your dedicated support channel, or email us at support@escape.tech.