Skip to content

DAST

#34 · Enhanced Scanning Capabilities through Insomnia Collections & WP-JSON Schema support 🌐

We're excited to share a significant expansion in our Dynamic Application Security Testing (DAST) capabilities. Escape now supports a broader range of input formats, catering to diverse API testing needs and environments. πŸ› οΈ

Expanded Input Support πŸ”

  • Insomnia Collections: Extend your DAST capabilities to include Insomnia Collections, enabling seamless security testing for those utilizing this popular API tool.
  • WP-JSON Schema: Specifically for WordPress users, we now support WP-JSON Schema, enhancing security testing for WordPress-based APIs.
  • Continued Support for Existing Formats: Our DAST feature maintains its robust support for:
    • Swagger v2
    • OpenAPI v3
    • Postman Collection
    • GraphQL Introspection
    • GraphQL Schema

Why This Matters? 🌟

  • Broader Testing Reach: Cover a wider range of API formats, ensuring comprehensive security coverage across different platforms and tools.
  • Versatility in Security Testing: Adapt to various API design and documentation practices, offering flexibility and precision in security testing.
  • Ease of Integration: Smoothly incorporate these new formats into your existing security workflows, enhancing efficiency without compromising on thoroughness.

πŸ” Your Security, Our Commitment We continue to evolve our DAST capabilities to keep pace with the dynamic world of API security. Stay tuned for more updates as we constantly strive to provide top-tier security solutions.

Stay Proactive, Stay Secure!
#32 Β· Create New Applications in DAST Automatically via API! πŸ”₯

Exciting news from Escape Tech! You can now create new Applications in our Dynamic Application Security Testing (DAST) service directly through the API. This update is all about enhancing your workflow efficiency and simplifying your security testing process. πŸ› οΈ

Key Features of the API Route πŸ—οΈ

  • Flexible Application Settings: Define your application's specifics, like name, type (GraphQL or REST), and server URL.
  • Schema Customization: Provide your application's schema as a string or through a public schema URL.
  • Adaptable Scan Settings: Fine-tune your scans with settings like read/write access, customizable for safe production scans.
  • Authentication Support: Add authentication details for scanning, with options for different user names and authorization headers, or opt for no authentication.
  • Optional Repeater Use: Integrate a repeater if needed for your scanning requirements.

Advantages for You 🌟

  • Streamlined Integration: Add new applications to DAST quickly and efficiently via API.
  • Diverse API Support: Compatibility with both GraphQL and REST applications.
  • Tailored Scanning Options: Customize scans for precision and safety.
  • Simplified Authentication Setup: Easy setup for various authentication scenarios.

πŸ”— Check out the full API documentation here for detailed instructions and more info.

πŸ” Elevating Your Security, Simplified Our commitment to enhancing your security processes continues. This new feature demonstrates our dedication to providing flexible and comprehensive security solutions.

Happy Secure Coding!

#26 · 🎯 Elevate Your Security Focus with Risk Contextualisation and Prioritization

Introducing a pivotal feature in Escape that transforms your security management strategy: Risk Contextualization and Prioritization. Merging the power of Escape’s distinctive Inventory and DAST features, we’re enabling AppSec Engineers to pinpoint and prioritize what genuinely requires immediate attention.

πŸ™‰ The Objective:

Ensure that your focus and remediation efforts are efficiently targeted. An SQL Injection on a route manipulating sensitive data, especially when exposed to the internet, demands priority – and we ensure you recognize such issues upfront.

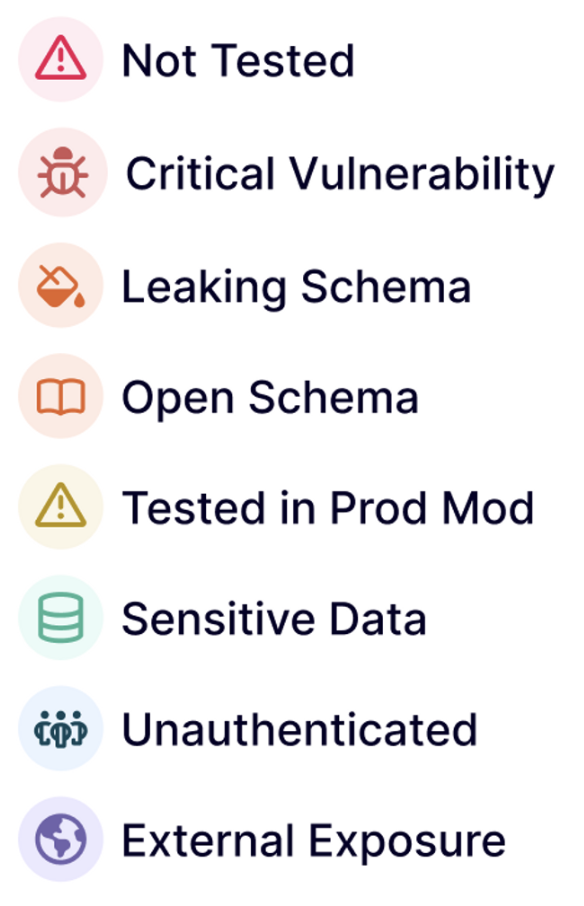
🚨 Risk Categories:

Navigating through risk becomes seamless with categorization that empowers you to identify and tackle vulnerabilities adeptly.

CleanShot 2023-10-03 at 11.57.25@2x.png

πŸ”Ž See it in Action:

Direct your attention and resources where it truly counts by honing in on critical, sensitive, and potentially exposed endpoints that could pose significant risks.

Let’s Continue Together:

Your security journey is our priority. With features designed to streamline your risk management, we're committed to offering a platform where your security endeavors are intuitive, strategic, and impactful. Share your experiences and let’s bolster our path towards sophisticated and accessible application security!

#25 Β· Escape for REST APIs in General Availability

πŸš€ REST API Scanning Now Available in Escape

We're thrilled to announce that Escape now supports GenAI-powered DAST Scanning in CI/CD, extending our capabilities to REST APIs alongside our existing GraphQL API offerings. Implementing security practices into your CI/CD pipeline has never been so straightforward!

βš™οΈ What's New:

  • 1. Extended API Support: Your REST APIs are now in safe hands with our advanced DAST scanning, which is now compatible with both REST and GraphQL APIs.
  • 2. Diverse Input Options: Catering to a variety of workflows, Escape accepts input from OpenAPI, Swagger, or Postman, with more options en route.
  • 3. Business Logic Testing: We're not just scanning - we're ensuring that your API's business logic and complex attack scenarios are thoroughly vetted.
  • 4. Comprehensive Security Tests: With more than 50+ security tests now supported, we're ensuring your APIs are fortified against vulnerabilities.

For a comprehensive view of our available security tests, check out our documentation.

πŸš— Taking it for a Spin:

Dive right into your API scanning and start fortifying your REST APIs alongside your GraphQL APIs. Ensuring comprehensive API security has never been this accessible or thorough.

In Closing:

As we pave the path toward robust API security, your inputs are invaluable. We're here to support your API – REST or GraphQL, and provide a secure, resilient environment for your applications. Share your feedback and let's continue this journey toward impregnable API security together!