Skip to content

Platform

#49 · Automated schema generation

We are excited to introduce our latest feature: automated schema generation for all your discovered APIs.

This feature allows you to generate your API schema and start scanning vulnerabilities immediately, reducing the time it takes to derive full value from Escape.

Why?

With this feature, we aim to solve this issue and provide you with the following benefits:

  • Efficiency: Through the automated generation of API schemas, either directly or via Git integration, we streamline the setup process for scans. The process involves parsing the AST from the code to dynamically generate detailed and accurate API schemas. This is particularly useful for organizations that may not have formalized API documentation. This not only saves time and effort for both security and development teams but also enables development teams to redirect their focus towards higher-value tasks.
  • Scalability: Automated schema generation allows you to effortlessly expand your scanning efforts across a large number of APIs. This is especially advantageous in environments with numerous microservices or APIs, where manual configuration would be impractical or time-consuming.
  • Access to Business Context: Automatically generated schemas provide more context to the API service. API service properties are of better quality when API specifications are available, enabling developers and stakeholders to gain a deeper understanding of the API's purpose, functionality, and intended business use. This enriched context ensures more in-depth scanning and facilitates smoother collaboration between security, development, and business teams.
  • Real-time Updates: With automated schema generation, scan configurations can be updated in real-time as your APIs evolve or new endpoints are added. This ensures that scans always reflect the current state of your APIs, eliminating the need for manual intervention to update configurations.

Getting started

Here's how you can quickly benefit from the automated specifications:

  1. If it's not yet done, add your new domain to your API inventory. For API services with a front-end, that's all there is to it! You'll see the following if your specification was generated automatically from the frontend code:
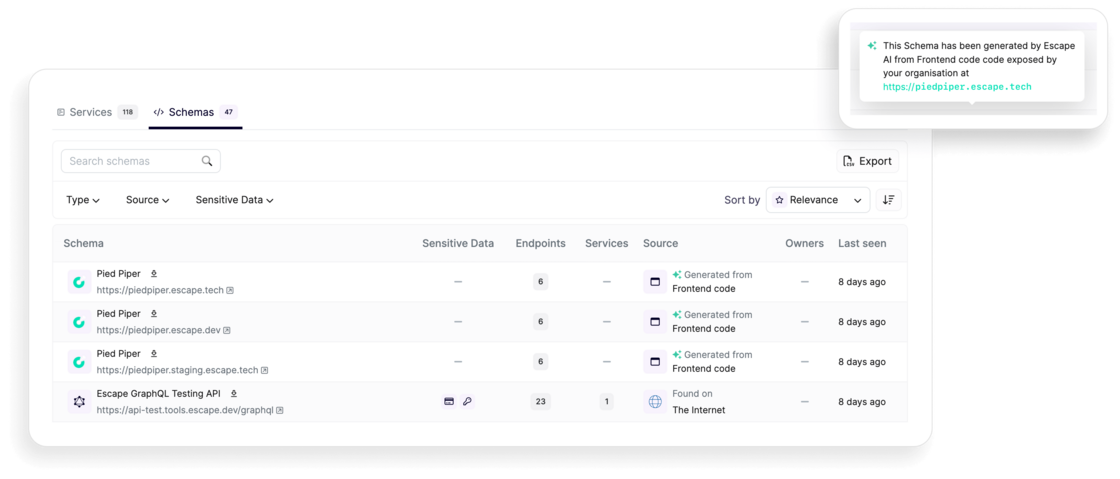
image.png

  1. For API services without a front-end, you need to set up integration with your GitHub, GitLab, or BitBucket. Navigate to your API inventory settings, then click on "Integrations" or simply select "Connect" from the "Connected Integrations" callout located in the top-right corner:
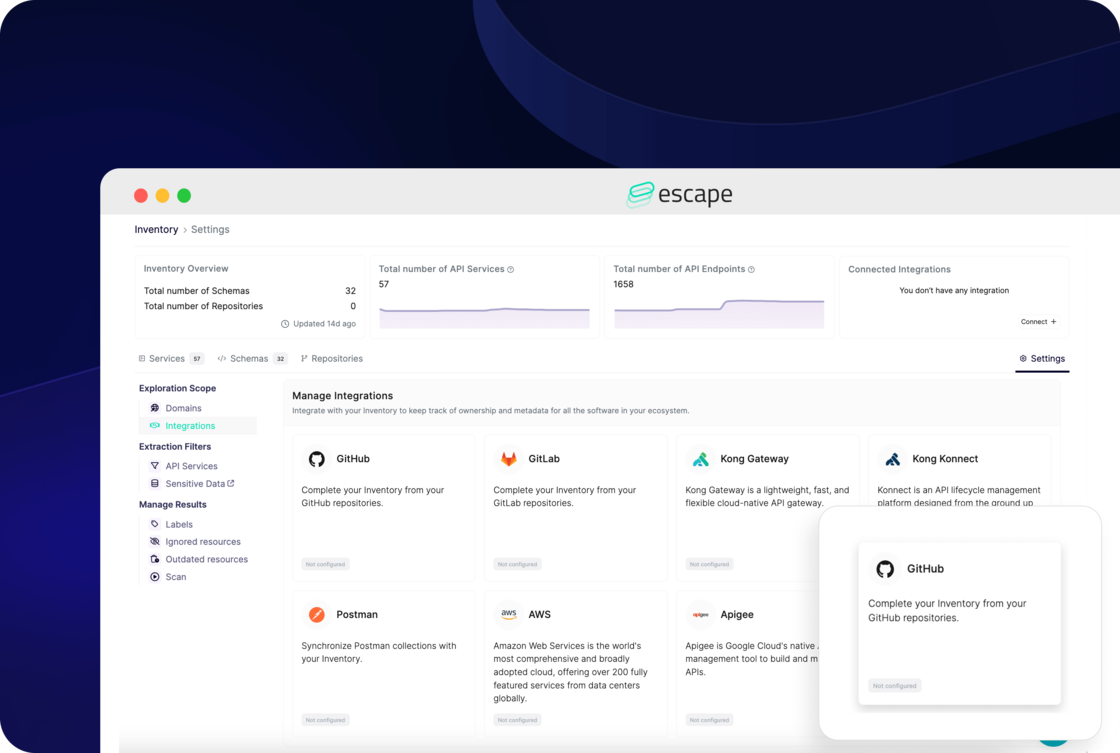
image.png

Then, enter the required information, like an access token for the integration of your choice. Below is example for GitHub:
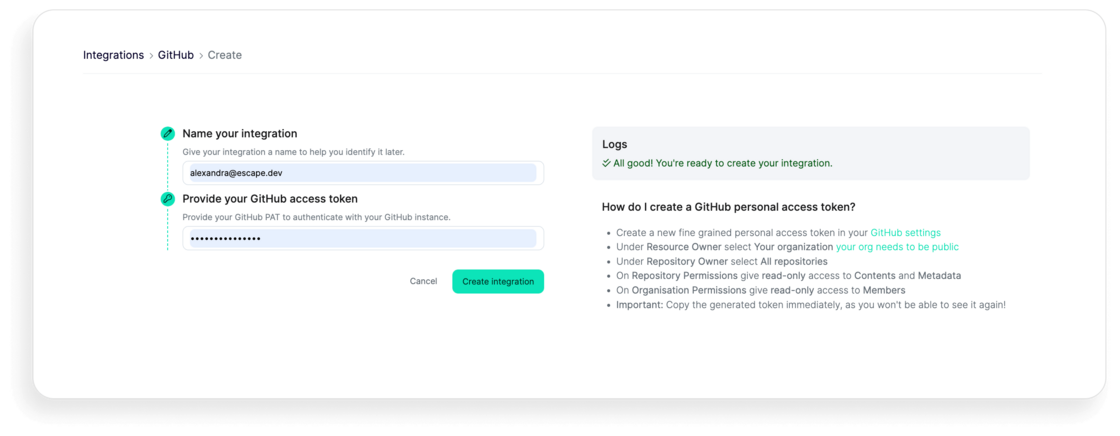
image.png

With these new updates, you should be able to run your security scans automatically once API endpoints are discovered by Escape, without the need to upload your API specs. Try it out for yourself!

#48 · Enhanced User Interface and Expanded Gateway Integrations

We understand that our users need a seamless, intuitive, and efficient interface to maximize their productivity. That’s why we’ve been hard at work redesigning our user interface to better meet your needs. Our latest updates are designed to enhance your interaction with our platform, making it more user-friendly and visually appealing.

What's new

Streamlined Menu

New Menu Structure: We've reorganized the menu to provide quicker access to your most frequently used features and functions.

Inventory

The inventory menu now includes:

  • All Services
  • Schemas
  • Repositories
  • Settings - Direct access to add new domains, integrations, and other settings.

Inventory API and Endpoint Naming: We’ve improved the visibility and naming of APIs and corresponding endpoints. Find these updates under Inventory -> All Services Dashboard.

As a reminder,

  • API Service: An application that provides a set of API Endpoints.
  • API Endpoint: A specific path exposed by an API Service.

Evidence Tab: Your Inventory's API schemas side panel now includes an evidence tab with corresponding JSON files.

All Risks Menu

Business-Critical Risks: Quickly access business-critical risks with the new All Risks menu.

Vulnerability Prioritization Funnel: Now located under All Risks -> Issues.

Exposed Secrets Management

New Location: Exposed secrets are now found under All Risks instead of Inventory. Secrets are categorized into Inventory Secrets and Scan Secrets.

Custom rules

New Location: Now available under Security Scan -> Custom Rules.

Enhanced Security Scan Menu

Comprehensive Security Options: The security scan menu now includes:

  • Tested Applications
  • Custom Rules
  • CI/CD Scans

New Integrations

Axway Gateway Integration: Integrating Axway Gateway with Escape's Inventory enhances your API management capabilities. This integration allows for comprehensive synchronization of API data between Axway Gateway and Escape, ensuring enhanced visibility and advanced security monitoring of your APIs. View documentation for more.

Mulesoft Gateway Integration: Integrating Mulesoft Gateway with Escape's Inventory enhances your API management capabilities by leveraging the extensive API management features of Mulesoft. This integration allows for seamless synchronization of API data between Mulesoft Gateway and Escape.View documentation for more.

#47 · Vulnerabilities prioritization funnel: Focus on what matters

We are excited to announce updates to our vulnerability prioritization funnel, which will help you focus on vulnerabilities that pose a real danger to your business.

What's new

You can now track the number of issues at each stage as they progress up and down the priority funnel:

  • All security issues across your applications
  • Issues still pending resolution (i.e., not dismissed by your team)
  • Issues exposed externally
  • Issues discovered without implemented authentication
  • Critical issues
  • Issues with high business impact

For each stage, you'll find the vulnerability group and the corresponding number of issues. You can filter out each vulnerability and view the details of how it was found.

Why

Before we added this feature, security engineers had to manually filter out high, medium, and low vulnerabilities without enough visibility into what needed to be fixed in their business context. This process could have been time-consuming, and business-critical API security issues could have slipped through the cracks —where should you focus your attention first?

With this feature, we aim to solve this issue and provide you with the following benefits:

  1. Enhanced Focus: By visualizing the vulnerabilities at each stage of the prioritization funnel, your team can easily identify and prioritize critical issues that pose the greatest risk to your business.
  2. Streamlined Workflow: Instead of manually tracking vulnerabilities, the automated funnel enables your team to efficiently allocate resources towards resolving high-priority issues, optimizing workflow and response times.
  3. Improved Risk Management: With greater visibility into the types and quantities of vulnerabilities, you can make more informed decisions regarding risk mitigation strategies, ensuring better protection for your applications and sensitive data.
  4. Accountability and Transparency: By documenting the journey of each vulnerability through the prioritization stages and its owner, you foster accountability within your team and promote transparency in your security processes, facilitating collaboration and communication. Overall, this feature empowers your organization to address security threats efficiently!

Getting started

  • In the left-hand sidebar, click Reporting.
  • In the reporting view, click on the See all issues.

And that's it! You'll get a complete view of the total amount of all your vulnerabilities down and up the prioritization funnel. Try it for yourself!

#46 · API Inventory: New features and improvements

We are excited to announce our updates to API discovery and inventory, which will give you even more capabilities to achieve API governance with ease.

What's new

  • Now, you can discover not only the APIs and API schemas of your primary organizational domain but also those of all your subsidiaries automatically, thanks to the AI-powered domain suggestion feature.
  • Next, we've expanded the API characteristics available in the view associated with each endpoint. Now, Escape offers visibility and a comprehensive understanding of the following:

👉 The characteristics of the API and its environment, including:

  • Production, staging, or development API
  • API type and framework: REST, GraphQL, SOAP, WebSocket, gRPC…
  • Cloud hosting: AWS, Azure, OVH…
  • Associated firewall: Cloudflare, AWS ELB, Azure WAF…

👉 The risks associated with each exposed API:

  • Leakage of sensitive data
  • External exposure
  • Disclosure of API schema
  • Lack of authentication or authorization
  • Critical vulnerabilities

👉 The business logic of the API:

  • Automatic generation of the Schema (OpenAPI) by generative AI
  • Detection of API creation date, API versions, and schema changes
  • Detection of Shadow APIs, Zombie APIs, Legacy APIs
  • Detection of similar or duplicate APIs

👉 The API owner:

  • Business unit
  • Code owners

👉 The context of API usage, including:

  • Third-party services: Gitlab, Jira, Confluence, SQL Database, Keycloak…
  • Internal service, classified based on its usage

👉 The type of sensitive data exchanged, including:

  • Personally Identifiable Information (PII): Including but not limited to Social Security numbers, full names, and email addresses.
  • Financial Information: Such as credit card numbers, bank account details, and transaction histories.
  • Authentification tokens and Secrets: For example, API keys, JWT tokens, and encryption keys.

A complete list of supported data types can be found on the Advanced Usage/Data Types Reference page.

Why?

Here are the key benefits of new API discovery and inventory capabilities :

  • Streamlined oversight: By automatically uncovering APIs across multiple organizational domains and subsidiaries, you are now empowered with a simplified approach to ensuring comprehensive oversight without manual effort.
  • Business strategic analysis: You can now gain deeper insights into the context and business logic of APIs. Make strategic decisions based on comprehensive understanding and analysis and align those decisions with the organization's goals and objectives.
  • Proactive risk management: Identify and address potential risks associated with each API before they are released in production and escalate.
  • Enhanced accountability: With clear ownership of each API, responsibility can be assigned more effectively. It also helps you to promote a culture of accountability within the organization.

These features collectively provide comprehensive insights into API usage contexts, sensitive data exchanged, and associated risks, enabling your organization to make informed and timely strategic decisions.

#44 · Introducing "Activity": A Timeline & Communication Hub for Your Security Management 🕒

We're excited to unveil a pivotal new feature within the Escape platform: Activity. This addition revolutionizes how you monitor and interact with elements like Security Issues, Sensitive Data Leaks, and Discovered API Endpoints. It's designed to enhance transparency and collaboration within your team, making security management more interactive and informed.

Key Features of the Activity Tab:

  • Comprehensive History Tracking: The Activity feature provides a detailed timeline that includes every action taken related to an issue—when it was first seen, last seen, ignored, and more. This historical insight ensures you're always informed of the status and evolution of each security concern.
  • Collaborative Commenting: An essential function of Activity is the ability to leave comments directly on an issue. This feature is particularly beneficial for actions like "Comment & Ignore," where context can be crucial for future reference or for team members who may revisit the issue.

Why the Activity Tab Matters:

  • Enhanced Visibility: By offering a detailed history of actions and interactions, Activity ensures that every team member is on the same page. This clarity eliminates confusion and enhances the decision-making process.
  • Improved Collaboration: Security is a team effort. The ability to comment and communicate within the context of specific issues or discoveries fosters a collaborative environment, making it easier to share insights, justify decisions, and coordinate actions.
  • Streamlined Security Workflow: Activity simplifies the workflow for managing security issues by centralizing communication and history in one accessible location. This consolidation helps in quickly understanding the story behind each issue and facilitates faster, more informed responses.

Take Control of Your Security Narrative:

With the introduction of Activity, you're not just tracking security issues; you're creating a narrative around them. This feature empowers your team to better manage and communicate around security concerns, turning isolated incidents into opportunities for learning and improvement. Dive into the Activity and discover how it can transform your approach to API security management.

#43 · New Integrations & One-Click Configuration: Seamless Workflow Enhancements 🌐

Escape is excited to announce a significant update designed to streamline your workflow: New Integrations and One-Click Configuration. This update simplifies the integration process, making it more intuitive than ever to connect Escape with your tools and services.

Effortless Integration Setup 🖱️

  • One-Click Configuration: We’ve made setting up integrations a breeze with our new one-click configuration. Say goodbye to complex setup processes and hello to instant connectivity.
  • Detailed Logging: To ensure that connections are straightforward to debug, we’ve implemented detailed logging. This feature makes it easy to troubleshoot, ensuring your integrations work smoothly.
  • Enhanced Connectivity with Access Internal Networks: A groundbreaking feature of our new integrations is the ability to connect to internal networks. This enhancement broadens the scope of what's possible with Escape, offering more flexibility and coverage for your security needs.

Expanded Inventory Integrations 🛠️

Focusing on Inventory, our aim is to enrich your automated API inventory with even more integrations. Alongside existing connections with Github & Gitlab, we're thrilled to introduce integrations with:

  • Kong & Kong Gateway: Seamlessly connect with Kong ecosystems to enhance your API management and security.
  • AWS & Azure: Leverage integrations with major cloud service providers to ensure comprehensive visibility and security across your cloud infrastructure.

Why This Matters 🚀

The introduction of one-click configuration and new integrations significantly enhances your experience with Escape, making it easier, faster, and more comprehensive:

  • Simplify Your Workflow: Reduce setup time and effort, allowing you to focus on what matters—securing your APIs.
  • Enhanced Debugging: With detailed logging, diagnosing and solving integration issues is more straightforward, ensuring a smooth operational flow.
  • Broader Integration Coverage: The addition of new integrations, especially with internal networks, Kong, and major cloud providers, ensures a more extensive and enriched API inventory. This comprehensive coverage is crucial for a thorough security posture.

Embrace the simplicity and power of Escape’s new integration capabilities. Streamline your security workflow today and unlock the full potential of your API inventory management.

#42 · Elevate Your GraphQL Security with Escape's New AI-powered Scanner 🐦‍🔥

Escape proudly introduces our latest innovation in API security - the New GraphQL Scanner, a state-of-the-art tool designed specifically for GraphQL Security Assessment. As the sole pure-player in GraphQL security and a proud member of the GraphQL Foundation, Escape stands at the forefront of safeguarding GraphQL APIs.

Leading GraphQL Security 🔍

  • Top-Ranked Solution: Escape is recognized as the top-ranked GraphQL Security solution, setting the standard for comprehensive assessments.
  • Advanced AI Technology: Utilizing cutting-edge artificial intelligence, our scanner delves deep into the security of GraphQL APIs, identifying vulnerabilities with unmatched precision.
  • Extensive Test Suite: With over 100+ security tests, including 25 that are specifically tailored to GraphQL business logic, our tool offers unparalleled coverage. Explore our tests in detail here.

Unmatched Testing Capabilities 🛠️

  • Exclusive GraphQL Support: Escape's scanner is the only tool designed to thoroughly assess GraphQL APIs, providing depth in testing that’s second to none.
  • Versatile Scan Modes: Catering to diverse needs, our scanner features different modes, including a rapid "surface scan" for OWASP TOP 10 assessments and a "business logic mode" perfect for CI/CD pipelines. Learn more about our scan modes here.
  • CI/CD Ready: Our business logic mode is optimized for CI/CD environments, ensuring comprehensive business logic scans in just a few minutes - ideal for fast-paced development cycles.
  • Scalability for Large APIs: The scanner is adept at handling extensive APIs, including Federated ones, ensuring no API is too large for a thorough security review.

Why Choose Escape for GraphQL Security? ✨

Choosing Escape's New GraphQL Scanner means not only employing the most thorough tool on the market but also aligning with a solution that’s been crafted by the leading experts in GraphQL security. Whether you're looking to conduct quick assessments or in-depth reviews, our scanner provides the flexibility, depth, and precision needed to secure your GraphQL APIs effectively.

Elevate your GraphQL security with Escape and ensure your APIs are protected by the best. Join us in redefining the standards of API security and stay ahead of threats with our advanced GraphQL scanner.

#41 · AI-Driven Prioritization: Smarter Security Insights for Immediate Action 🧠

We're thrilled to introduce a groundbreaking addition to the Escape platform that's set to transform how you prioritize security issues within your organization. Leveraging the power of Artificial Intelligence, we've created a new section that synergizes results from both the Inventory and Testing phases, offering you a Smart Prioritization of issues based on their risk level.

From Overwhelming to Actionable ✨

  • Beyond Numbers: Move away from daunting lists like "I have a total of 34 injection vulnerabilities in my organization" to precise, actionable insights. For example, the AI helps you pinpoint critical issues such as "Among those injection vulnerabilities, one is on a publicly-accessible payment API exposed on the internet that manipulates personally identifiable information". This clarity ensures you know exactly what needs your attention first.
  • Risk-Level Awareness: Understand the gravity of each vulnerability in the context of your organization's unique environment, allowing you to allocate your resources more effectively and mitigate the most significant threats first.

Why Smart Prioritization Matters 🚀

  • Focused Efforts: Concentrate on fixing the most critical vulnerabilities that pose the greatest risk to your organization, ensuring a stronger security posture.
  • Efficient Resource Allocation: Maximize the impact of your security team by directing their efforts toward mitigating high-priority issues.
  • Faster Response Time: With clear prioritization, respond to and remediate vulnerabilities more swiftly, reducing the window of opportunity for attackers.
  • Strategic Planning: Use AI-driven insights for strategic planning and strengthening your overall security framework, focusing on areas of highest risk.

Leverage AI for Enhanced Security 🛡️

This AI-driven approach to prioritizing security issues represents a significant leap forward in cybersecurity management. By integrating smart prioritization into your security strategy, you're not just reacting to threats; you're anticipating them and acting with precision and confidence. Transform your security posture with Escape's AI-driven insights and stay one step ahead in safeguarding your organization's assets.

#40 · Fine-Tuned Alerting & Notifications: Stay Ahead of Security Concerns 🔔

Escape is thrilled to introduce our enhanced Alerting and Notifications system, now with seamless integrations including Teams, Slack, Discord, Webhooks, and Email. This upgrade is designed to keep API owners in the loop with real-time alerts on new issues identified during testing, and notifications when a new API is discovered by our Inventory system.

Tailored to Your Needs 🛠️

  • Highly Configurable: Dive into a wealth of configuration options to tailor alerts and notifications to fit your specific needs. Whether you prefer detailed reports or succinct summaries, our system can be adjusted to your preferences.
  • User-Friendly: Despite its depth of options, our alerting system is incredibly straightforward to use, ensuring you can set up and customize your notifications without any hassle.

Stay Informed, Always 🌐

  • Immediate Notifications: Receive alerts as soon as new security issues are detected or new APIs are discovered, enabling swift action.
  • Comprehensive Coverage: Our system is designed to keep you informed on all fronts, from testing updates to inventory changes, ensuring you have a full overview of your API landscape.

Seamless Integration & Migration ✨

  • Widespread Integration: With support for popular platforms like Teams, Slack, Discord, and more, you can receive alerts through the channels you use every day.
  • Default Notifications: To ensure immediate value, we've set up default notifications for all organizations, getting you started right out of the box.
  • Smooth Migration: For users of our previous notifications system, we've seamlessly migrated your settings, ensuring a smooth transition with no action required on your part.

Empowering Your Security Posture 🚀

Our fine-tuned Alerting and Notifications system is not just an upgrade; it's a transformation in how you stay informed about your API security. It's designed to be as powerful or as simple as you need, ensuring

#39 · Enhanced Reporting: 8 New Graphs for Unmatched Security Insights 📊

We're excited to unveil a significant upgrade to our Reporting features, designed to provide you with a comprehensive overview of your organization's security posture. Our enhanced reporting now includes 8 insightful graphs, each crafted to offer a deeper understanding of your API security landscape.

Explore the New Graphs 📈

  • Open Security Issues: Get a clear snapshot of unresolved security vulnerabilities within your organization.
  • Open and Closed Issues Over Time: Track how security issues are being resolved over time, highlighting your team's responsiveness to threats.
  • Most Vulnerable APIs: Identify which of your APIs are most at risk, allowing for prioritized and focused security efforts.
  • Average API Health: Understand the overall health of your APIs at a glance, with scores based on security assessments.
  • Security Issues Over Time: Visualize how security issues fluctuate over time, revealing trends and the effectiveness of your security measures.
  • Most Critical Issues: Focus on the most pressing security vulnerabilities with a graph highlighting the issues that require immediate attention.
  • Top Endpoints to Scan Next: Get recommendations on which endpoints to prioritize in your next scans, based on vulnerability assessments.
  • Active Scan Coverage: Measure the extent of your scanning efforts across your API landscape, ensuring comprehensive security coverage.

Why This Matters for Your Security 🛡️

  • Proactive Security Management: Armed with these insights, you can proactively manage your organization's security posture, addressing vulnerabilities before they can be exploited.
  • Data-Driven Decisions: Make informed decisions on where to allocate resources, focusing on areas with the most significant security impact.
  • Trend Analysis: Understand how security trends evolve over time, enabling you to adjust your strategies to emerging threats.
  • Comprehensive Overview: Gain a holistic view of your organization's security health, fostering a culture of transparency and continuous improvement.
  • Efficiency and Prioritization: Streamline your security efforts by prioritizing the most critical issues and vulnerable APIs, ensuring optimal use of your time and resources.

Embrace the Power of Insightful Reporting 🌟

With these new graphs, Escape arms you with the tools you need to secure your APIs effectively. Embrace the benefits of enhanced reporting and take your organization's security to the next level. By understanding your security landscape in depth, you can foster a more secure, resilient, and efficient API ecosystem.