Skip to content

Platform

#119 · Bulk Edit Assets, Issues and Profiles

You can now perform bulk actions across assets, issues, and scan profiles directly from their respective pages. Apply tags, update statuses, and keep your inventory organized without repetitive manual work - built specifically for teams managing complex or high-volume environments.

What’s new

1.All Assets page:
  • Bulk assign tags: Organize assets more efficiently by applying relevant tags to multiple items at once.

  • Bulk update status: Quickly categorize assets as Monitored, False Positive, Out of Scope, or Deprecated with a single action.

    ![Screenshot 2025-07-30 at 14.02.04.png](320466-bulk-edit-assets-issues-and-profiles/03-185-8be8f491d8c260b4276d8e2843cb1c9ec2298f56.png)
    
2.All Issues page (when grouped by None):

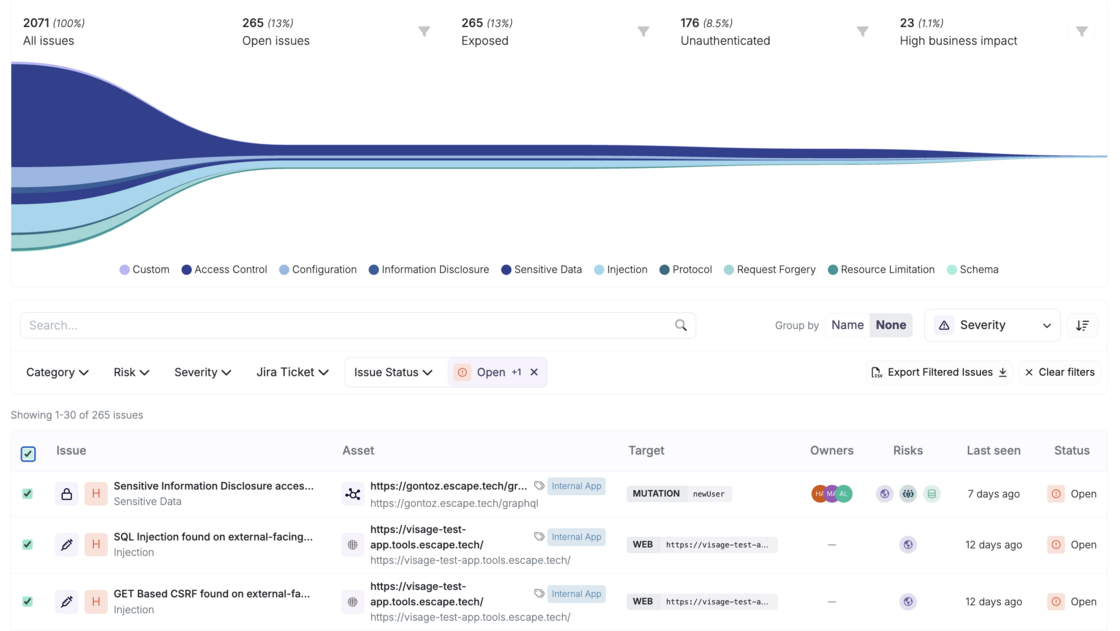
Easily update the status of multiple issues at once—set them as Open, Need Manual Review, Resolved, False Positive, or Ignored with a single click.

Screenshot 2025-07-30 at 13.20.45.png

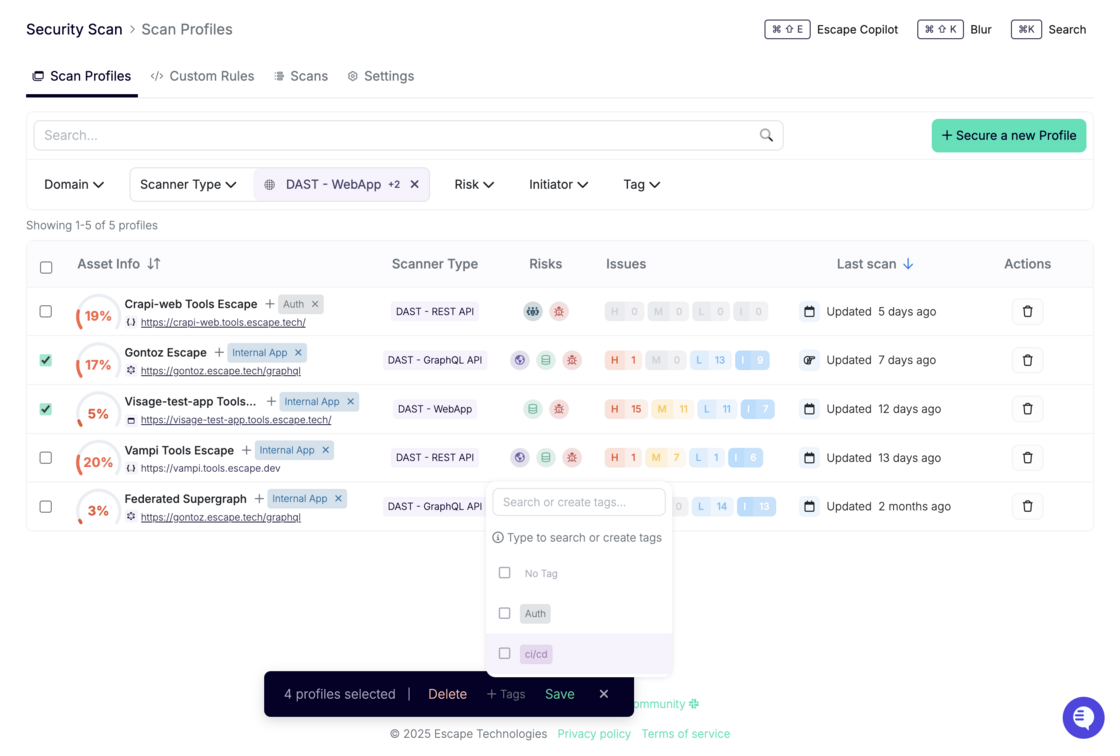
3.Scan Profiles page:
  • Bulk assign tags: Organize assets more efficiently by applying relevant tags to multiple items at once.

new.png

These improvements are designed to streamline your workflow, especially in large-scale environments—so you can maintain a clean, structured inventory without the repetitive manual work.

It’s easy for our team to add more bulk actions if your AppSec team requires it. Got any feedback? Reach out to your dedicated Escape contact!

#114 · Meet Escape Copilot: Automate App and Scan Management via MCP

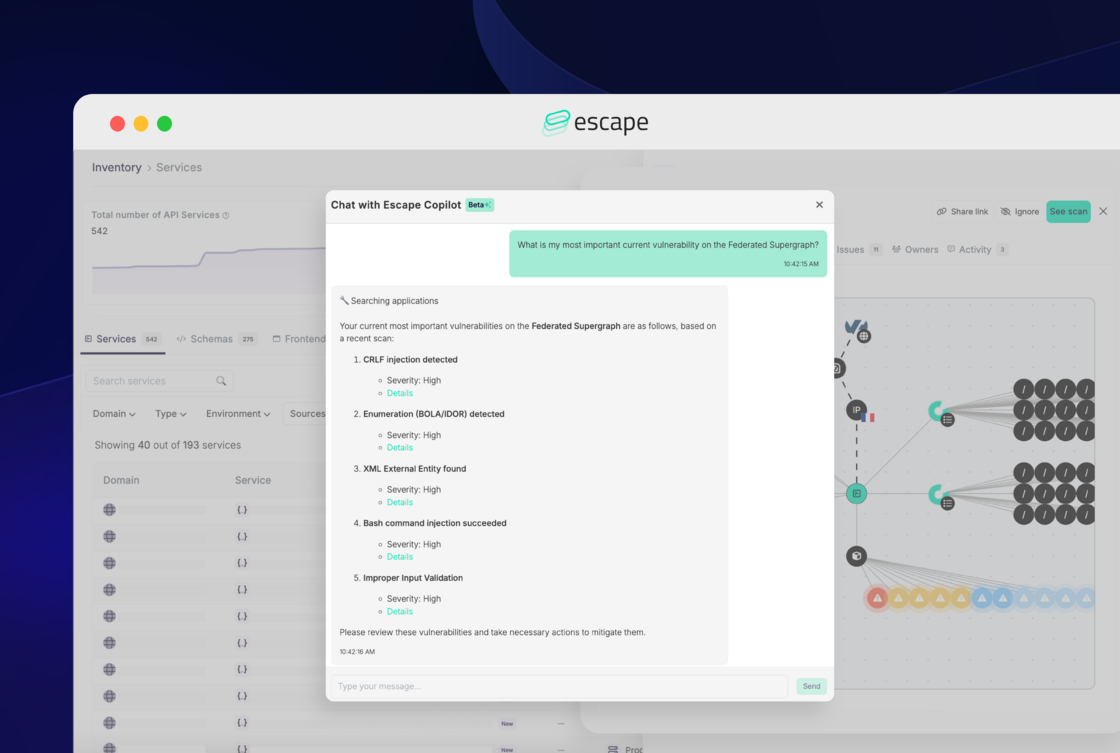
We’re introducing Escape Copilot (in Beta), a new AI-powered assistant designed to help your security team work more efficiently with the Escape platform.

Copilot-most-important-vuln.png

Powered by the Model Context Protocol (MCP) on the Escape Public API, Copilot understands your unique security setup and helps you get more done in less time by simplifying everyday workflows like managing scans and tracking assets.

It’s especially useful if you:

  • Juggle many services or microservices
  • Run regular scans across multiple apps and environments
  • Need instant access to domain, issue, or posture information

You can learn more about Escape Copilot and read answers to the most common questions (including data privacy and model training) in our official announcement.

What can Escape Copilot do today? (Beta)

Below are the core capabilities available in the beta release:

Application Management
  • Create Applications: Define new applications by specifying essential details such as name, URL, type (e.g., GraphQL, REST, Frontend), location, and configuration.
  • Update Applications: Easily update application details, including name, location, and scheduling options.
  • List Applications: Retrieve a complete list of all applications managed within your platform.
  • Get Application Details: Obtain specific details about any application using its unique ID or name.
Scan Management
  • Start Scans: Trigger scans to identify vulnerabilities.
  • Check Scan Status: Monitor ongoing or recent scans.
  • List Scan Issues: Access detailed reports highlighting vulnerabilities and security issues detected during scans.
  • List Scan Events:Review chronological events associated with scans, providing insights into the scanning processDomain Management
Domain Management
  • Create Domains: Register new domains (FQDNs) to be monitored.
  • Delete Domains: Remove unnecessary or outdated entries.
  • List Domains: View all domains under management.
  • Get Domain Details: Retrieve detailed information about specific domains using their IDs.
Access Scan Archives
  • Get Exchange Archive URLs: Retrieve access to scan exchange archives for further investigation.

Powered by the Model Context Protocol (MCP)

Escape Copilot runs on the Model Context Protocol (MCP) using the Escape Public API. This means every interaction is tightly scoped to your organization’s actual configuration and security data — no pre-training, no external inference, no guesswork.

Copilot only responds based on what’s accessible through your scoped Escape Public API access, ensuring:

  • No external data storage
  • No training on your data
  • Context-aware, action-ready results

It follows strict cybersecurity best practices and puts user privacy first. We recommend sharing only the data necessary for effective interaction.

Try Escape Copilot today

Escape Copilot is now available in beta to all customers!

Just press Cmd + Shift + E (or Ctrl + Shift + E on Windows) to activate Copilot in-app.

Feel free to play around, and we're looking forward to your feedback!

#113 · Updated Handling of Secrets & Sensitive Data in Escape

We’re rolling out a significant evolution in how we surface exposed secrets and sensitive data - laying the groundwork for a new era of AI-powered secret detection and prioritization that will change how you protect your most critical assets.

What’s new

We’ve retired the standalone Exposed Secrets tab in All Risks and the Sensitive Data tab from individual scan reports to unify these findings as standard issues within your risk ecosystem. This shift aligns sensitive data detection with the broader risk framework, making it easier for you to:

  • Understand and prioritize secrets and sensitive data exposures in the proper business context,
  • Quickly triage and remediate through familiar workflows,
  • Leverage powerful filtering and search — by test category, risk type, asset, and more.

How to access your secrets today:

  • Re-running scans will surface new true positives and previously undetected secret combinations.
  • At the application level, visit the Issues tab and filter by Category → Sensitive Data
  • Globally, use All Risks filtered by Risk Type → Sensitive Data

What’s Next: Bringing Inventory-Based Secrets Into the Fold

Currently, secrets discovered through Inventory, Inventory Frontends, and Inventory Integrations are temporarily hidden due to an ongoing migration effort. We’re actively working to restore full visibility here, seamlessly integrating these findings into the new sensitive data experience.

This migration is foundational, enabling us to introduce powerful AI capabilities soon — dramatically improving accuracy, context-awareness, and proactive remediation.

Our new approach will be more than a UI change, we want to genially improve how you handle sensitive data detection:

  • You’ll be able to distinguish what truly matters, differentiating public vs. private data, dev vs. production environments, and sensitive personal info vs. less critical disclosures. For example, leaking personal emails with SSNs is flagged with higher severity than a few generic professional emails.
  • Access validation: You’ll see whether exposed secrets can actually grant access (e.g., AWS keys, DB credentials), reducing false positives.
  • AI-driven prioritization: Leveraging a proprietary machine learning algorithm that is not trained on customer data, Escape will adapt over time, only surfacing sensitive data alerts that pose genuine risk in relevant contexts, learning from your feedback and historical issue handling.

#110 · Escape CLI Now Available for Windows

The Escape CLI is now officially supported on Windows, making it easier for security teams to automate scans across their environments.

With the CLI, you can manage applications, integrations, private locations, and scans. Use it to trigger scans manually or integrate Escape directly into your CI pipelines - streamlining security testing at scale.

You can install Escape CLI using the following command:

powershell -c "irm https://raw.githubusercontent.com/Escape-Technologies/cli/refs/heads/main/scripts/install.ps1 | iex"

To check if the CLI is installed, you can run the following command:

escape-cli version

Full Escape CLI documentation and usage examples.

#108 · Improved API Graph for Better Visibility and Clarity

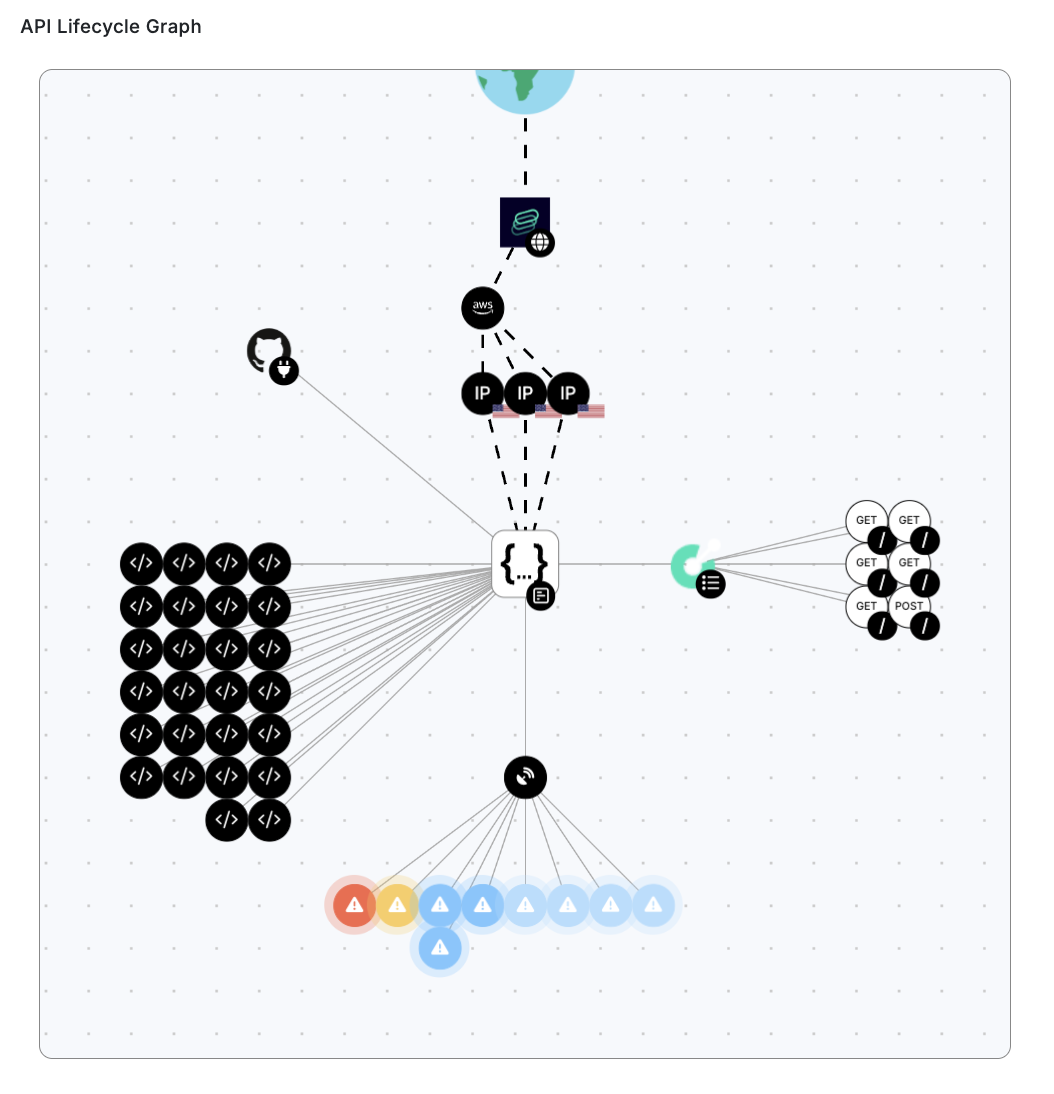
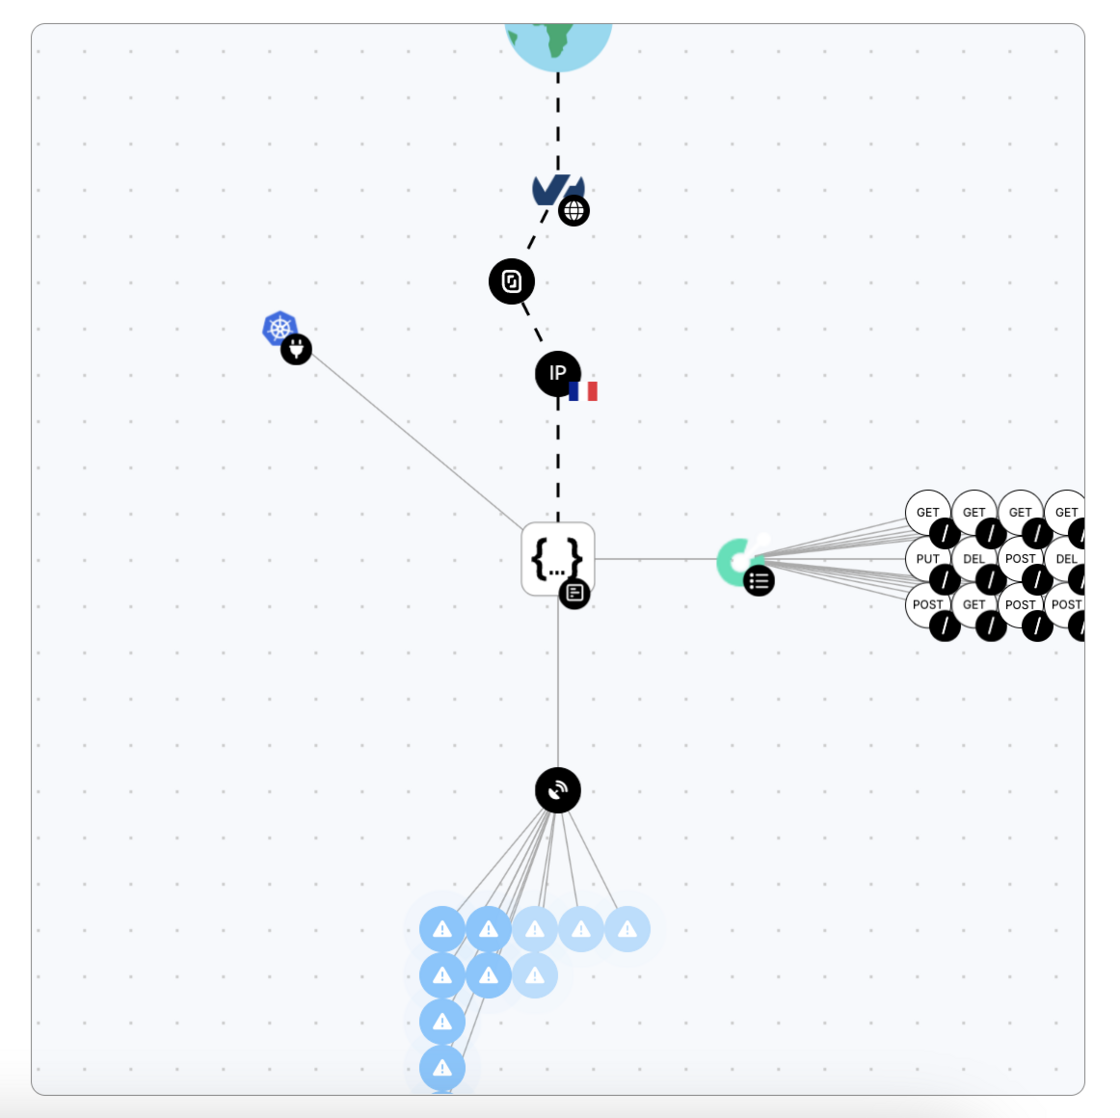
We’ve made several updates to the API Graph to improve readability and help teams assess their API landscape more efficiently:

  • HTTP methods are now displayed per endpoint, making it easier to distinguish between operations like GET, POST, PUT, and DELETE.
  • Security alerts are presented more clearly, allowing for faster identification and prioritization of issues.
  • Improved visibility into public exposure, so you can quickly determine whether an endpoint is accessible from the internet.

These enhancements make the API Graph more informative and actionable for everyday use. You can find a couple of examples below:

new-api-lifecycle-graph.png

new-api-lifecycle-graph2.png

For context on the original release of the API lifecycle graph, see this post.

#107 · Improved RBAC with Role- and Label-Based Permissions

We’ve expanded Escape’s Role-Based Access Control to give teams more precise control over who can access which applications and findings.

What’s new:

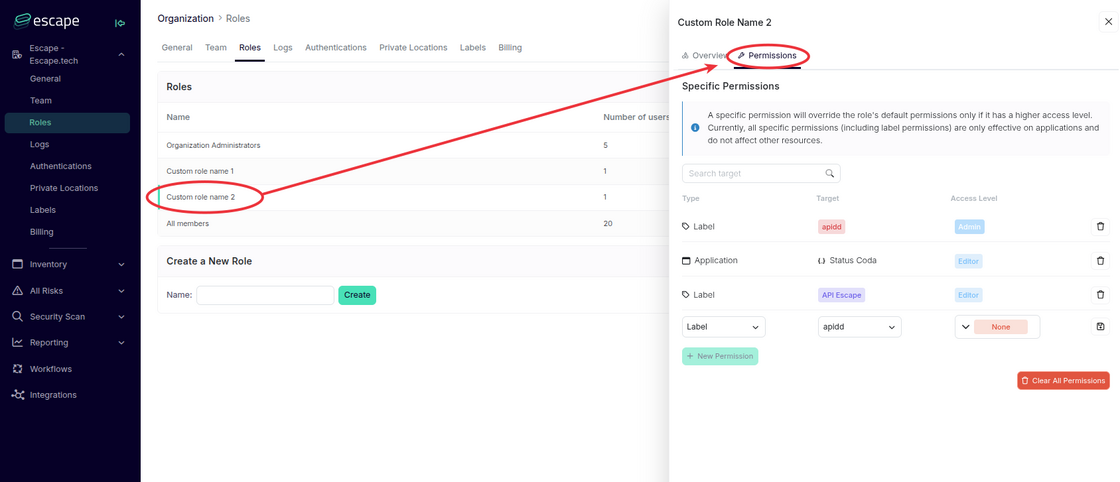
  1. New “Permissions” sub-panel within each role groupe

A new Permissions sub-panel is now available for each custom role group you’ve created (Accessible via Organization - Roles):

how-to-find-permissions.png

  • Previously, managing permissions was only possible from the global Permissions settings.
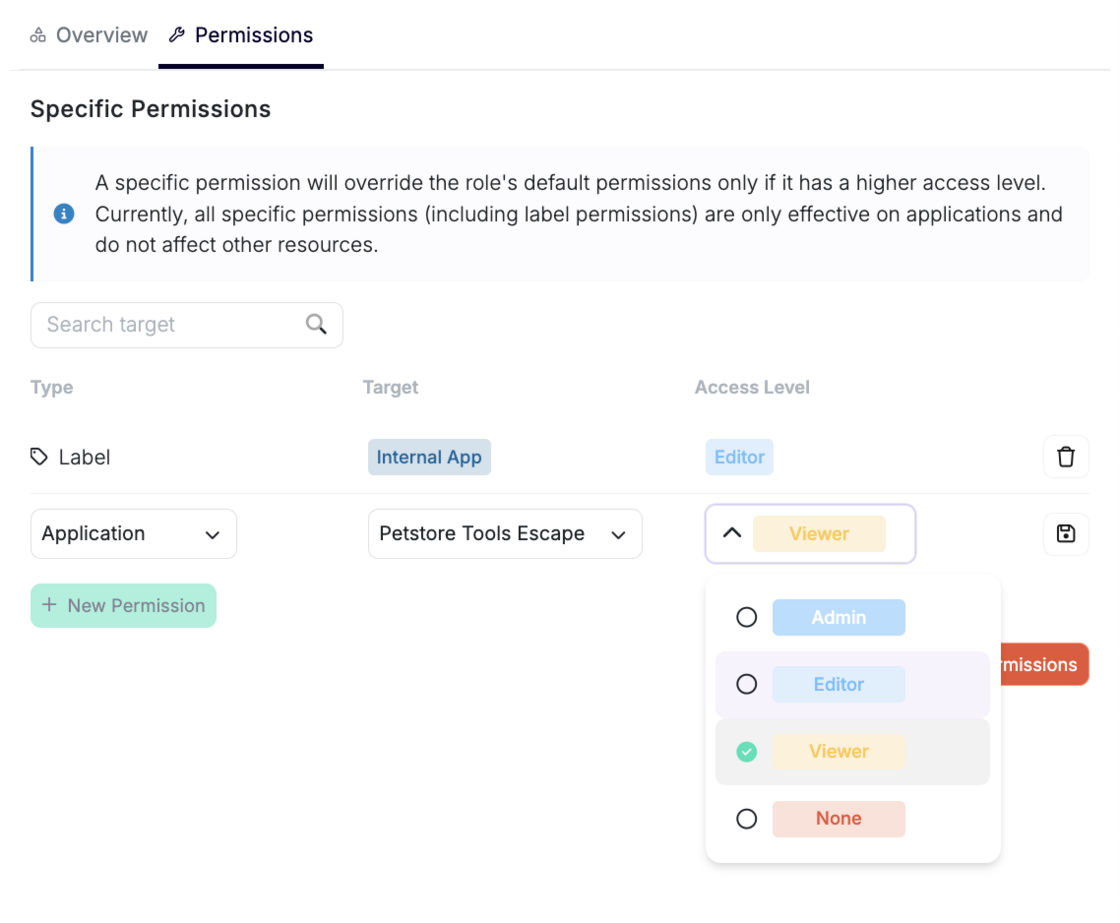
  • You can now define application-specific or label-specific permissions directly within each role type. permissions-new-escape.png

Note that a specific permission will override the role's default permissions only if it has a higher access level.

2. Label-Based Permissions

You can now assign access to groups of applications using shared labels - without giving full access to everything in those apps to the users of your choice.

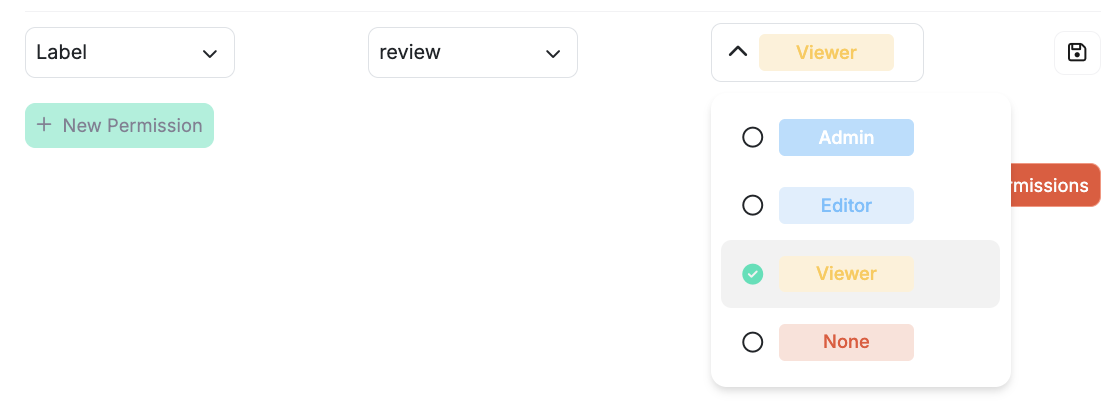
  • To create a label-based permission: click New Permission, select "label," choose a label name, and assign an access level (Admin, Editor, Viewer, None).

labels-permissions.png

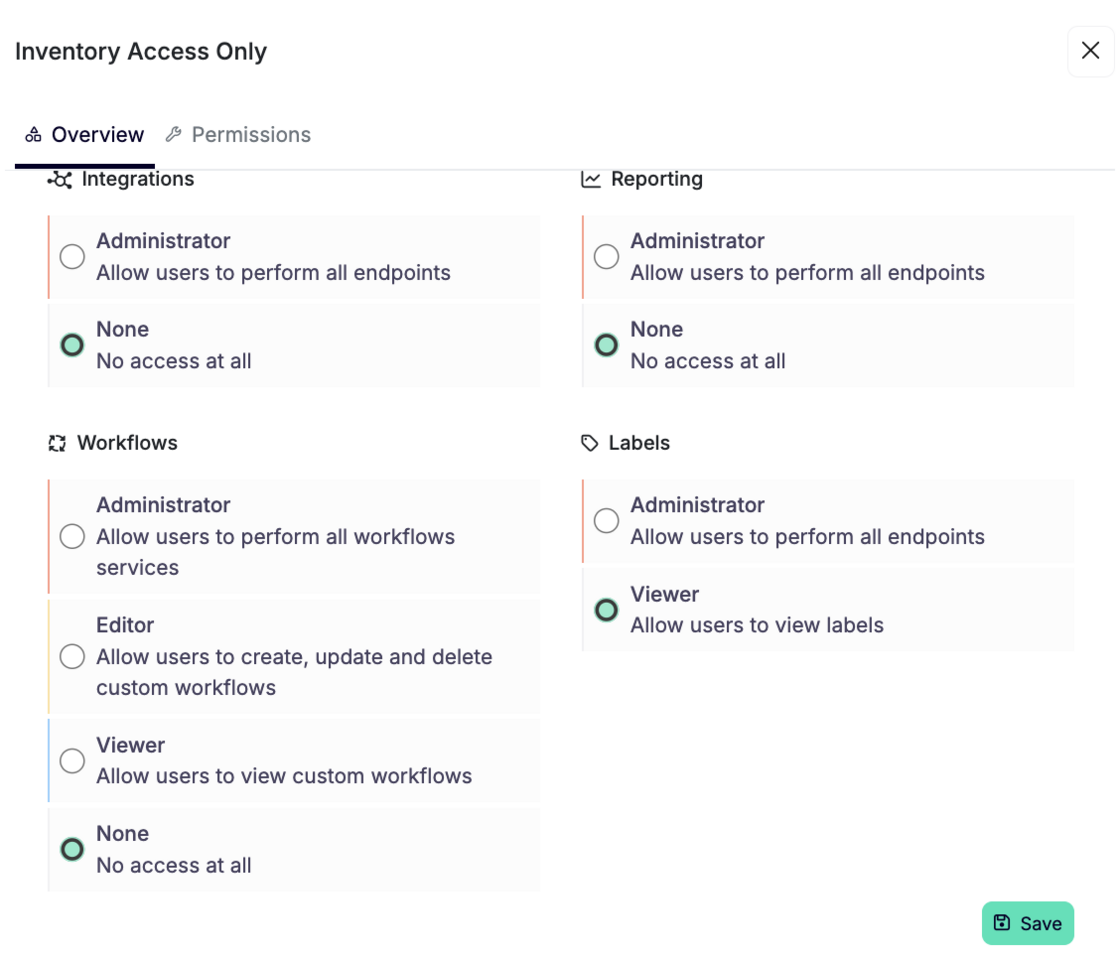
A new "labels" right has also been added to the existing Overview tab for each role type:

permissions-2.png

  • It allows you to define whether users can view or manage labels.
  • Set to Viewer by default.

How Permissions Work

  • Start by defining a base role type, then configure global permissions (e.g. Inventory, Integrations, Workflows). You can optionally add specific permissions tied to individual applications or labels.
  • Assign users to the appropriate role types based on their responsibilities.

Key Notes:

  • A specific permission will override the default role permissions only if it grants a higher access level.
  • Specific permissions, including label-based ones, only apply to applications—they do not affect unrelated resources.

Overall, these improvements let you:

  • Confidently onboard more teams and apps without compromising data boundaries.
  • Limit access to only what's necessary - reducing both risk and complexity.
  • Keep permission management scalable across growing organizations.

Learn more about full Escape Role-Based Access Control (RBAC) capabilities in our documentation.

#105 · From Alert to Action: Improved Jira Integration

We are excited to introduce an enhanced Jira integration designed to make your vulnerability management process even more seamless and efficient.

When setting up your Jira integration, you can now create multiple templates for ticket generation. Each template lets you specify the issue type, mapped to your organization's ticket types (e.g., Task, Subtask, Bug), and align Escape’s severity with your organization’s priority levels.
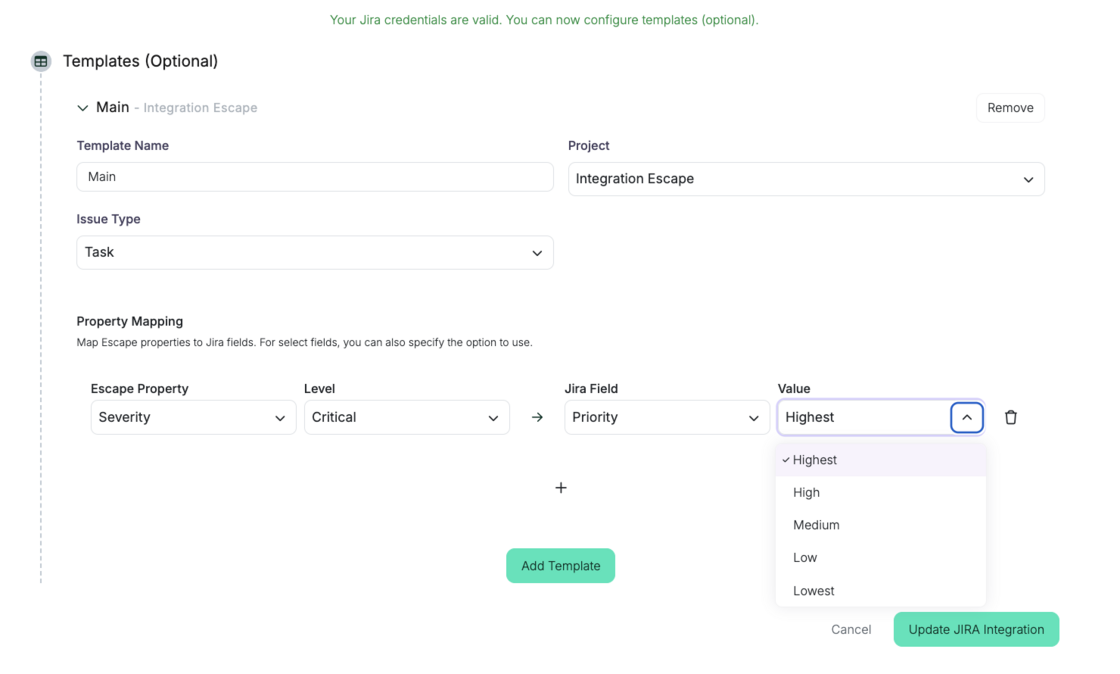
Screenshot 2025-04-22 at 12.09.05.png

Additionally, the templates will prefill most of the necessary information when creating a Jira issue from Escape, including

  • the issue name
  • description
  • cURL request(s) used
  • detailed remediation steps with a tailored development framework
  • a link to the scan

This ensures that every ticket is consistently created with relevant and accurate details each time.

We also hope that the ability to map Escape’s severity to your internal priorities will help you to streamline risk management, ensuring that your team can react swiftly based on your established thresholds!

How to Set Up the Integration:

If you haven’t set up the Jira integration yet, here’s how you can get started:

  1. Go to the Integrations Page: Click on Jira.
  2. Choose Add New Integration.
  3. Configure your integration:

  4. Name your integration.

  5. Add your Jira instance URL and API key.
  6. Enter the linked email associated with your Jira account (the one used to generate the API key).
  7. Validate Credentials: Click Validate Credentials to ensure your connection is working properly.

4.Once the credentials are validated, you can create and manage multiple templates.

The templates allow you to customize key fields such as:

  • Name
  • Project Name
  • Issue Type (based on the available types in your Jira instance)
  • Escape Severity Mapping to your internal priority system

Select and Associate a Template to Create and Send Jira Tickets

Once you've set up your templates, when you create a ticket associated with a vulnerability, you can easily select the appropriate template from the list you’ve created. This allows you to quickly send the preconfigured ticket to Jira with the correct issue type, severity, and all other relevant details.
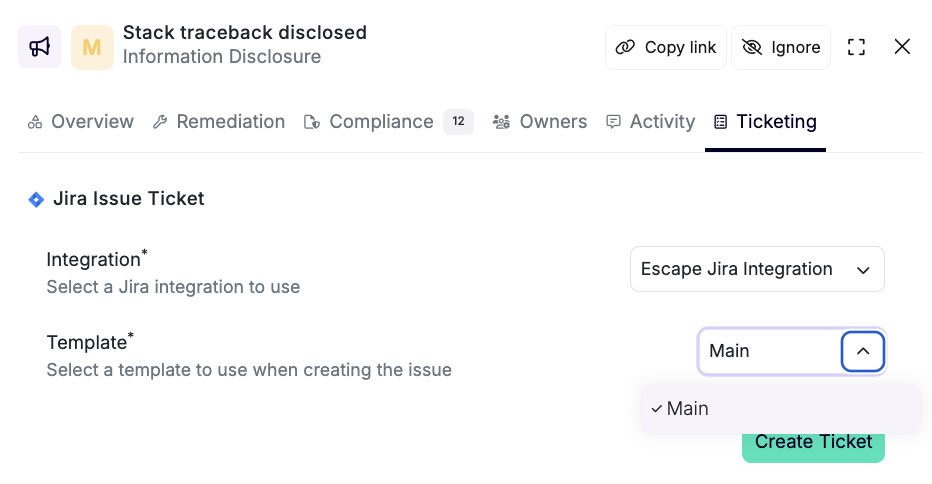
Screenshot 2025-04-22 at 12.13.43.png

Using Templates in Workflows:

One of the best parts of this update is the ability to use your templates directly within Escape’s workflows. For example, when a critical vulnerability is detected, you can automatically create a Jira ticket with the associated template. This helps you respond to high-risk issues promptly and ensures that all the necessary details are included from the get-go.
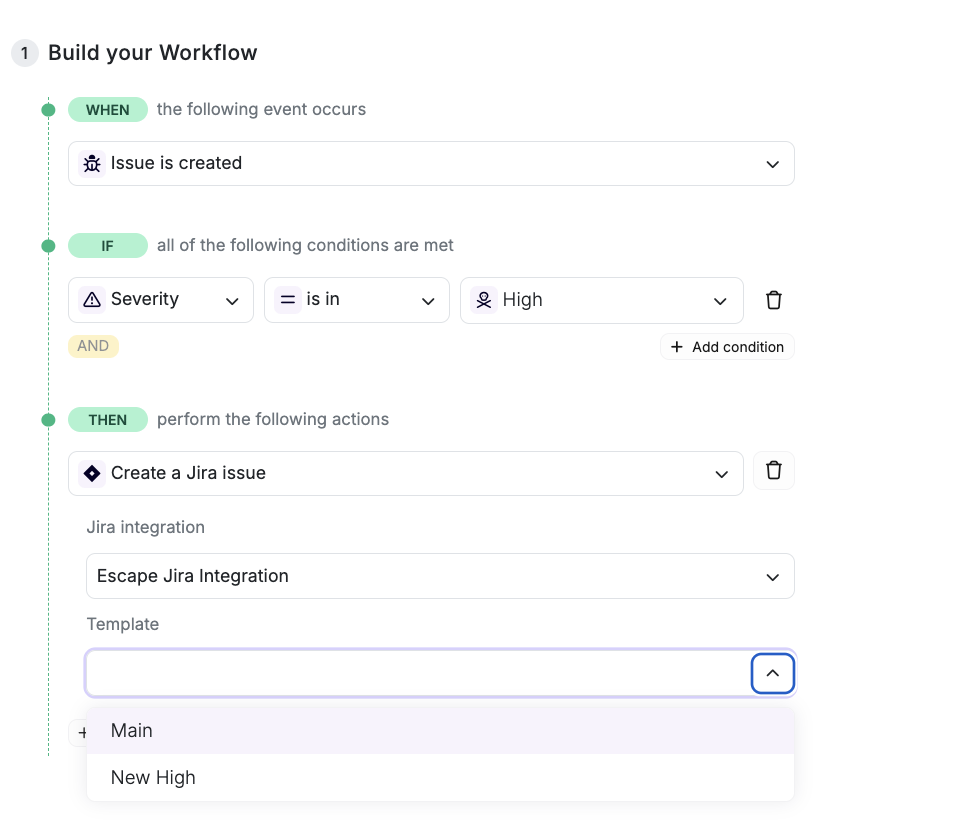
Screenshot 2025-04-22 at 12.21.49.png

On the Jira Side:

When the issue is created in Jira, you’ll see the pre-configured issue type and severity level mapped to your internal system, so everything is in place as per your organization's standards.
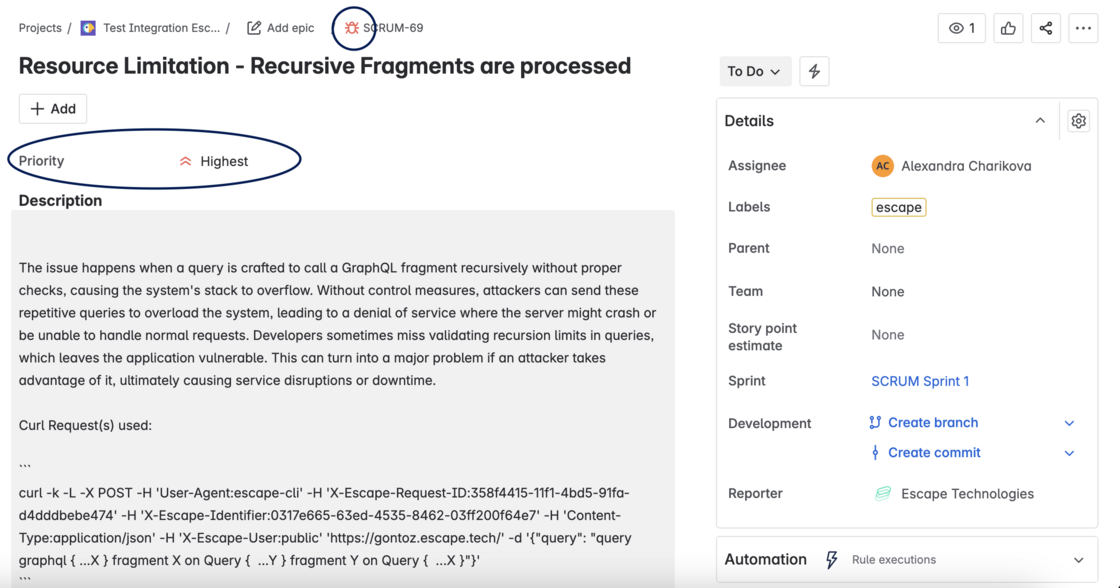
Screenshot 2025-04-22 at 13.08.14.png

With this update, we hope to help you make it easier than ever before to turn critical alerts into actionable Jira tickets. The next steps will provide even more flexibility when it comes to property field mapping.

Want to help improve our Jira integration? Reach out to our team via your dedicated Slack channel or email your dedicated contact!
#103 · Improved Logs Page & Updated Naming Conventions

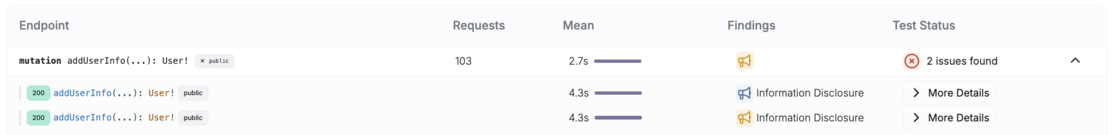
We’ve made some updates to the front-end views to improve overall clarity. While several names have been slightly changed, they won’t impact your overall experience. Additionally, the Logs page of each app now provides more detailed insights to help you monitor and optimize your app’s performance.

You can now see the Mean (Request Duration) for each endpoint (or GraphQL operation). This represents the average time it took for the scanner to send requests to the endpoint, giving you better visibility into scan execution and performance.

Screenshot 2025-04-10 at 12.05.02.png

#101 · Sensitive Data Detection in Front-End Applications

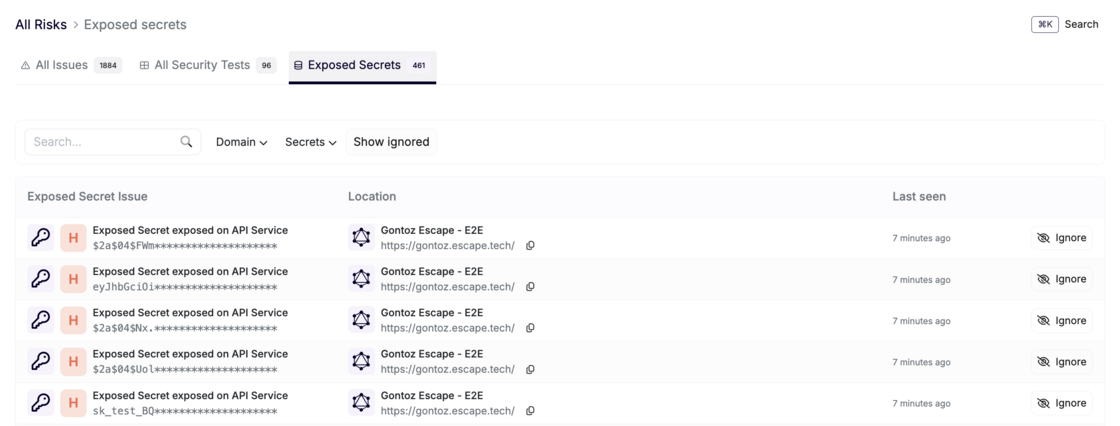
We’re excited to roll out a new feature that helps you catch sensitive data leaks in your front-end applications. Now, it’s easier than ever to find and manage exposed secrets across all of your apps.

What’s New?

Detect Sensitive Data Leaks in Front-End Apps

We’ve added the ability to scan front-end applications for any sensitive data leaks. This means you can now identify if secrets or credentials are unintentionally exposed in your apps.

View Exposed Secrets in One Place

All detected leaks will appear in the Exposed Secrets table, which you can find under the All Risks menu.

Screenshot 2025-04-10 at 11.47.20.png

Please note that this menu does not contain Personally Identifiable Information (PII) data. For a detailed view of exposed secrets and PII specific to each app, head to the Sensitive Data tab in the scanned application. This provides a more granular look at what’s been exposed and where.

With this update, we aim to help you catch sensitive data leaks early, so they don’t turn into bigger issues down the road!

#100 · We've Expanded Our SQL Injection Detection to More Frameworks!

We’re rolling out an exciting update: our platform now detects SQL injection vulnerabilities in more frameworks!

You’ll now get extra coverage for:

  • Propel
  • Illuminate
  • Doctrine
  • SQLAlchemy
  • MariaDB

This update makes it easier than ever to secure your apps across a broader range of technologies.